 www.pravda.com.ua
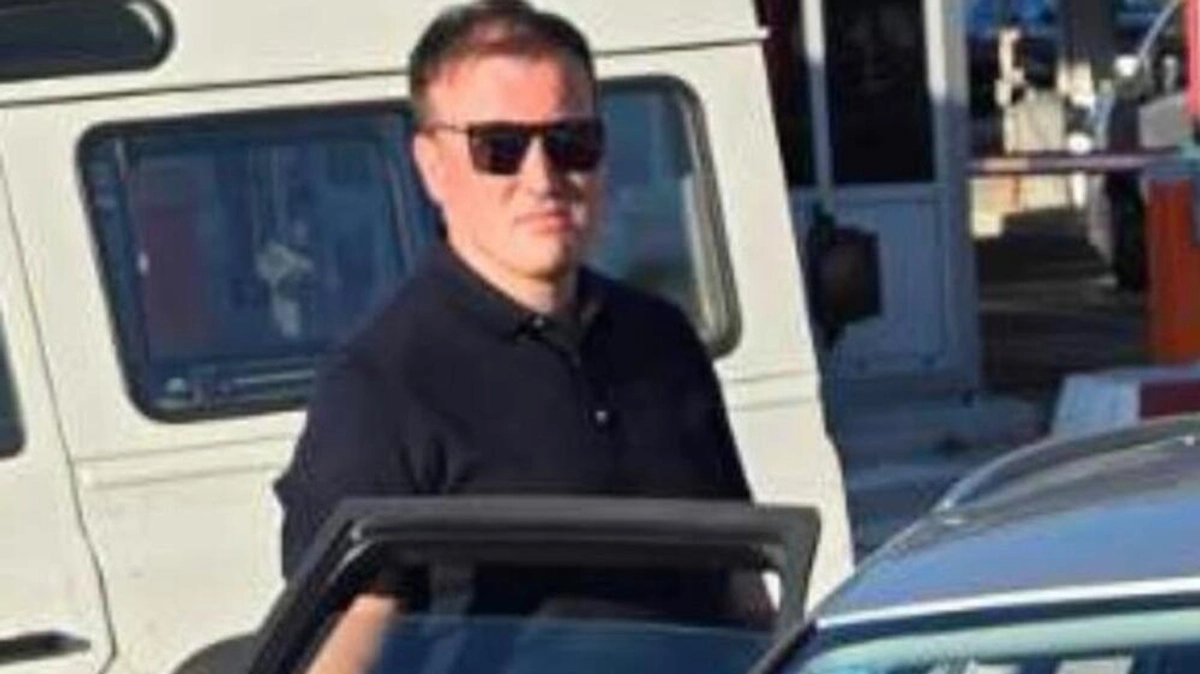
Montenegro Detains Russian Propaganda Network Founder Amid Security Concerns
Article Content

- •Mikhail Zvinchuk and four others were detained in Montenegro for national security reasons.
- •Zvinchuk is linked to Russian intelligence and has been sanctioned by the UK and US.
- •The operation aimed to prevent destabilization efforts in Montenegro.
Mikhail Zvinchuk, founder of the Rybar propaganda network, was arrested in Montenegro on October 9, 2026, along with his wife and three associates. The Montenegrin authorities acted on intelligence suggesting attempts to destabilize the country through hybrid warfare. Zvinchuk is linked to Russian intelligence and has been sanctioned by the UK and the US for his role in spreading Kremlin propaganda. The operation involved local police and the National Security Agency, and all detained individuals are set to be deported on national security grounds. The US State Department has offered a reward for information on foreign entities involved in election interference, including those associated with Zvinchuk. The Kremlin has expressed concern over the detention and is reportedly seeking his release. This incident may further strain Montenegro-Russia relations, which have been historically tense.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Following this threat?
Track Rybar in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What charges are Zvinchuk and his associates facing?
What actions have the US and UK taken against Zvinchuk?
How might this incident affect Montenegro's relations with Russia?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…