 Indiatoday.In
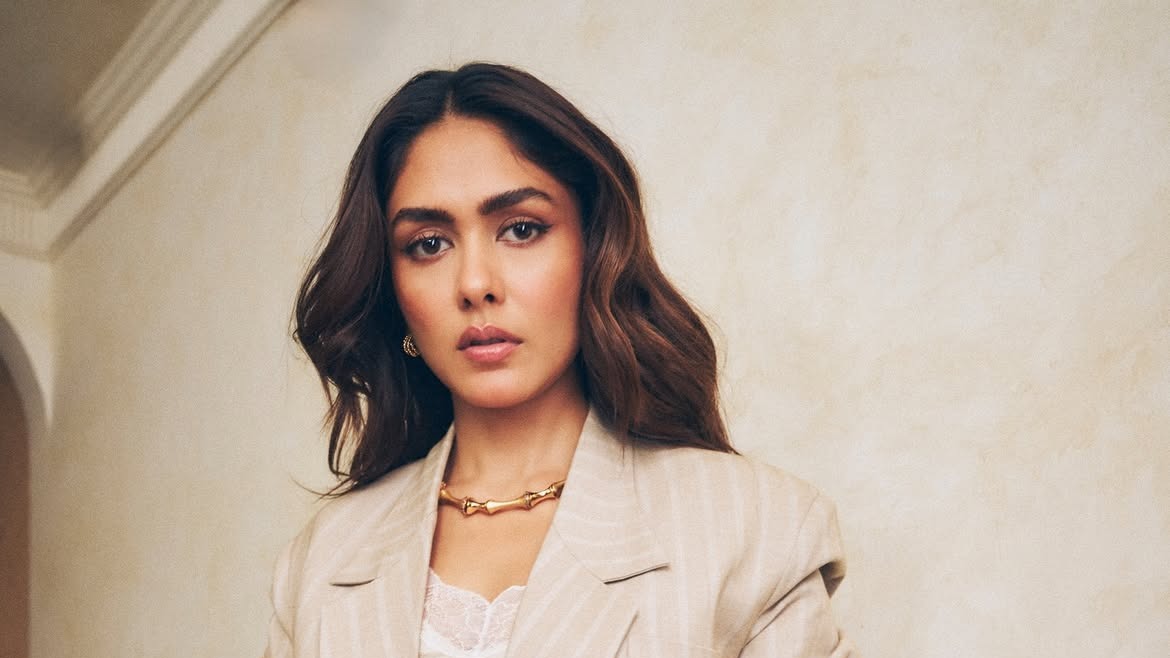
Mrunal Thakur Issues Legal Warning Against Deepfake Misuse
Article Content

- •Mrunal Thakur warns against deepfake content using her likeness, threatening legal action.
- •Her statement reflects growing concerns among celebrities about AI misuse in India.
- •The issue of deepfakes has prompted legal actions from multiple Bollywood stars.
Actress Mrunal Thakur has publicly warned against the creation and distribution of deepfake content using her likeness, labeling it as illegal and unacceptable. She stated that any further misuse of her identity would result in legal action, marking a significant moment in the ongoing debate about AI-generated content in India. Thakur's warning comes amid a rising trend of celebrities, including Akshay Kumar and Preity Zinta, taking legal measures to protect their identities from unauthorized AI manipulations. Her statement gained significant traction on social media, receiving over 1 million views. The issue of deepfakes has become a pressing concern in the entertainment industry, with many public figures calling for stricter regulations and legal protections against such misuse. Thakur's case highlights the broader implications of AI technology in identity theft and the need for legal frameworks to address these challenges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…