 Thevibes
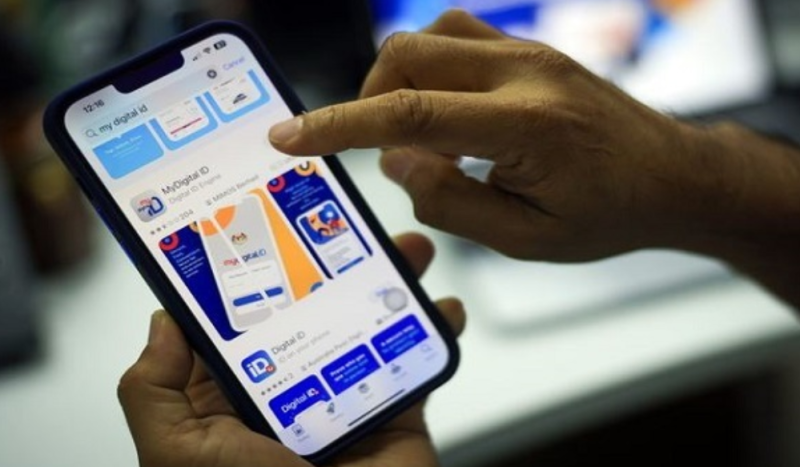
MyDigital ID Launches to Enhance Child Online Safety and Privacy
Article Content

- •MyDigital ID will be mandatory for social media users under 16 starting June 1, 2026.
- •The system verifies age without storing sensitive personal information or biometric data.
- •Strict data retention policies are enforced to protect user privacy and prevent misuse.
The Malaysian government is implementing MyDigital ID as a mandatory age verification system for social media users under 16, effective June 1, 2026. This initiative aims to protect children from cyber threats while safeguarding their personal data. Dr. Megat Zuhairy Megat Tajuddin, CEO of the National Cyber Security Agency (NACSA), emphasized that the system verifies age without requiring sensitive personal information, thus reducing the risk of data breaches and identity theft. MyDigital ID will not store physical ID copies or biometric data, relying instead on secure government-held records. The system acts as an intermediary, providing only necessary information to social media platforms. Strict data management policies are in place to ensure personal data is retained only as legally required. The initiative is part of a broader global trend towards enhanced online safety for minors.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…