 Bwpoliceworld
Navy Personnel Arrested for Espionage Ties to Pakistan's ISI
Article Content

- •A 24-year-old Indian Navy personnel was arrested for espionage for Pakistan's ISI.
- •The suspect allegedly shared sensitive naval information and transferred money to an ISI handler.
- •A related case involved another individual arrested for sharing Army information with ISI operatives.
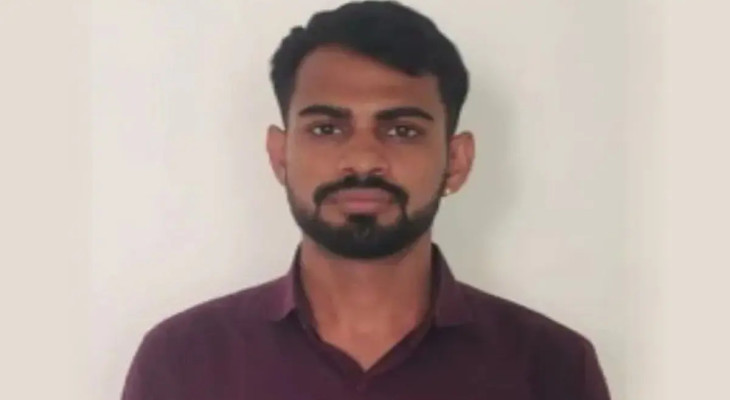
On March 11, 2026, the Uttar Pradesh Anti-Terrorism Squad (ATS) arrested a 24-year-old Indian Navy personnel, Adarsh Kumar, for alleged espionage activities linked to Pakistan's Inter-Services Intelligence (ISI). Kumar, a Seaman stationed in Kochi, Kerala, is accused of sharing sensitive information about India's defense infrastructure with a Pakistan-based ISI agent. Investigations revealed that he transferred money to the handler and shared photographs of naval assets. The ATS utilized electronic and physical surveillance to gather evidence leading to his arrest. In a related case, another individual was arrested in Rajasthan for passing sensitive information to ISI operatives after being honey-trapped. Both cases are under ongoing investigation, highlighting a concerning trend of espionage targeting Indian defense operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Indian Navy in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…