 Breakingdefense
NIOA and AeroVironment Partner for Loitering Munitions in Australia
Article Content

- •AeroVironment and NIOA signed an MOU to enhance loitering munitions capabilities in Australia.
- •The partnership aims to localize production and support for AeroVironment's one-way attack systems.
- •NIOA will serve as the local distributor and support partner for AeroVironment's systems.
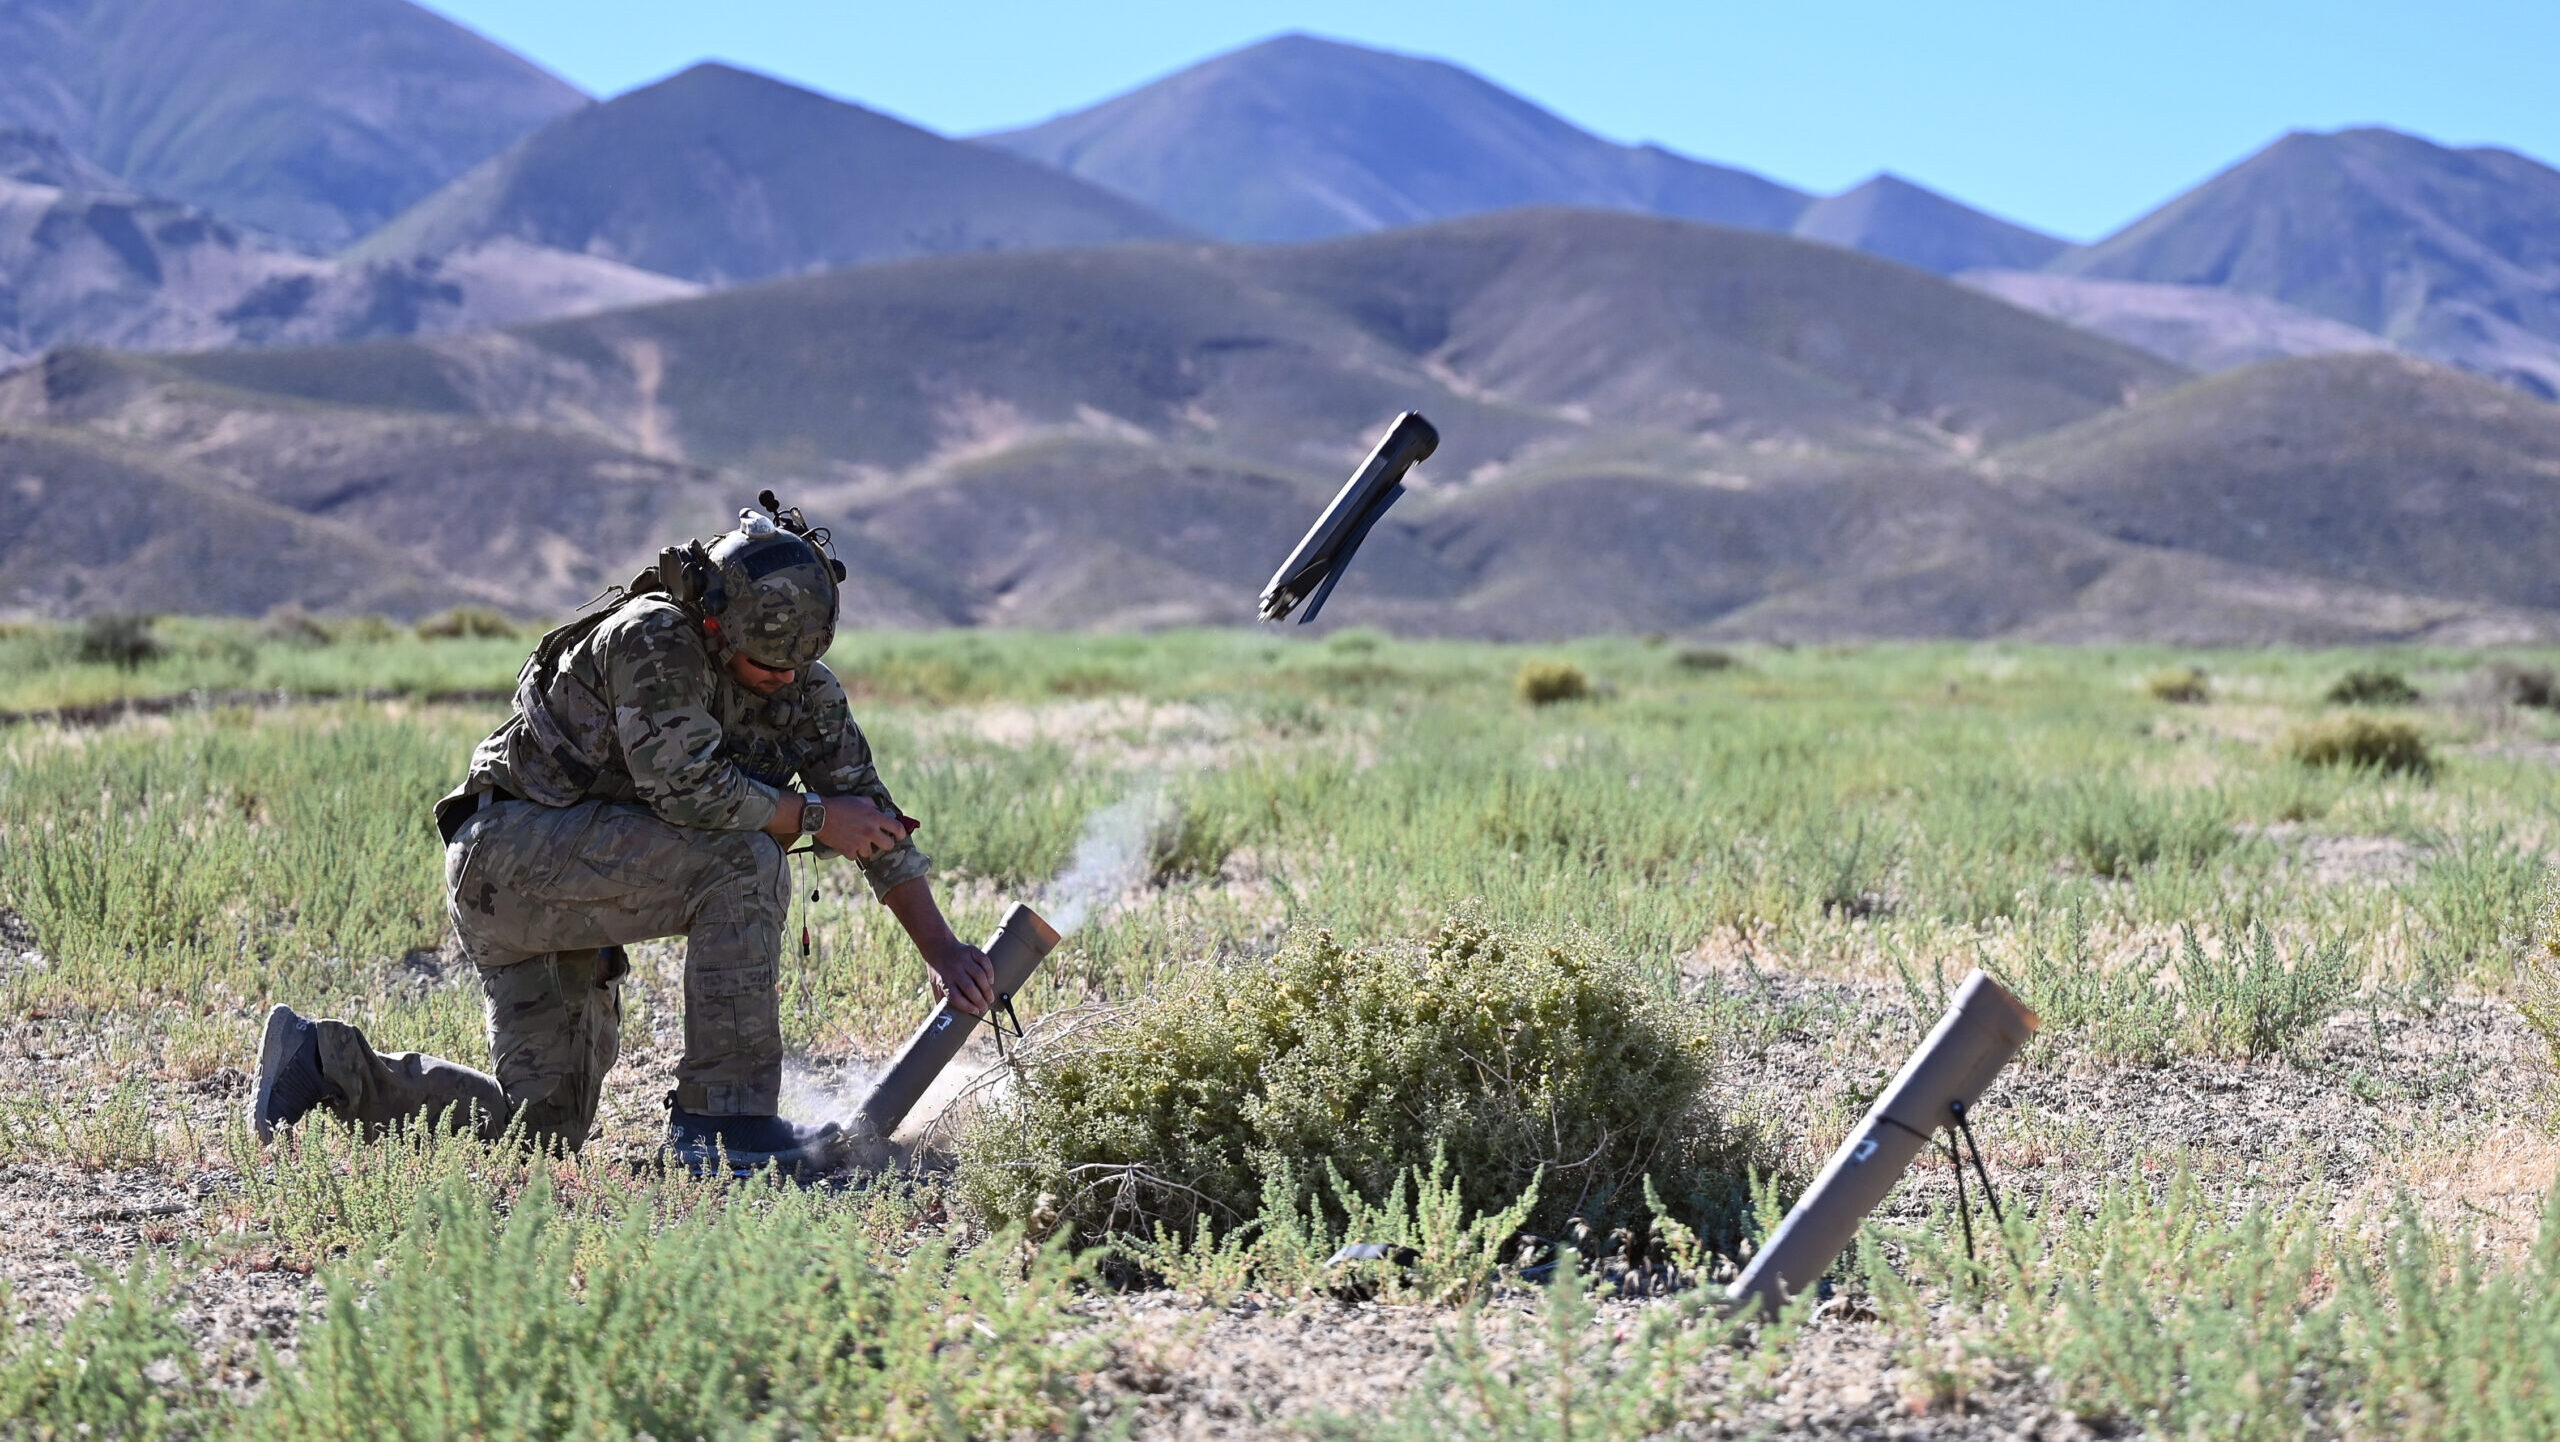
AeroVironment, Inc. and NIOA Australia have signed a memorandum of understanding to enhance the localization and co-production of AeroVironment's one-way attack systems in Australia. The agreement, announced during the LAND FORCES 2026 event, aims to combine AeroVironment's autonomous systems with NIOA's expertise in sovereign weapons and munitions. This partnership will explore local manufacturing, integration, and support for these systems, including the Switchblade family of loitering munitions. NIOA is positioned as AeroVironment's local partner for distribution and customer engagement, with plans to support the Australian Defence Force's requirements. The MOU is non-binding, and any future agreements will depend on applicable laws and approvals. The collaboration reflects a commitment to strengthening Australia's defense capabilities and expanding industrial cooperation between the U.S. and Australia.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track AeroVironment in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the purpose of the MOU?
Who will benefit from this partnership?
What are the next steps following the MOU?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…