 Army.Mil
NY Army Guard's Cyber Protection Team 173 Conducts Cyber Defense Exercise Against Simulated Threat
Article Content

- •CPT 173 conducted a cyber defense exercise against a simulated threat actor targeting utilities.
- •The exercise utilized the U.S. Cyber Command’s Persistent Cyber Training Environment.
- •Credential harvesting and ransomware were key attack methods simulated during the exercise.
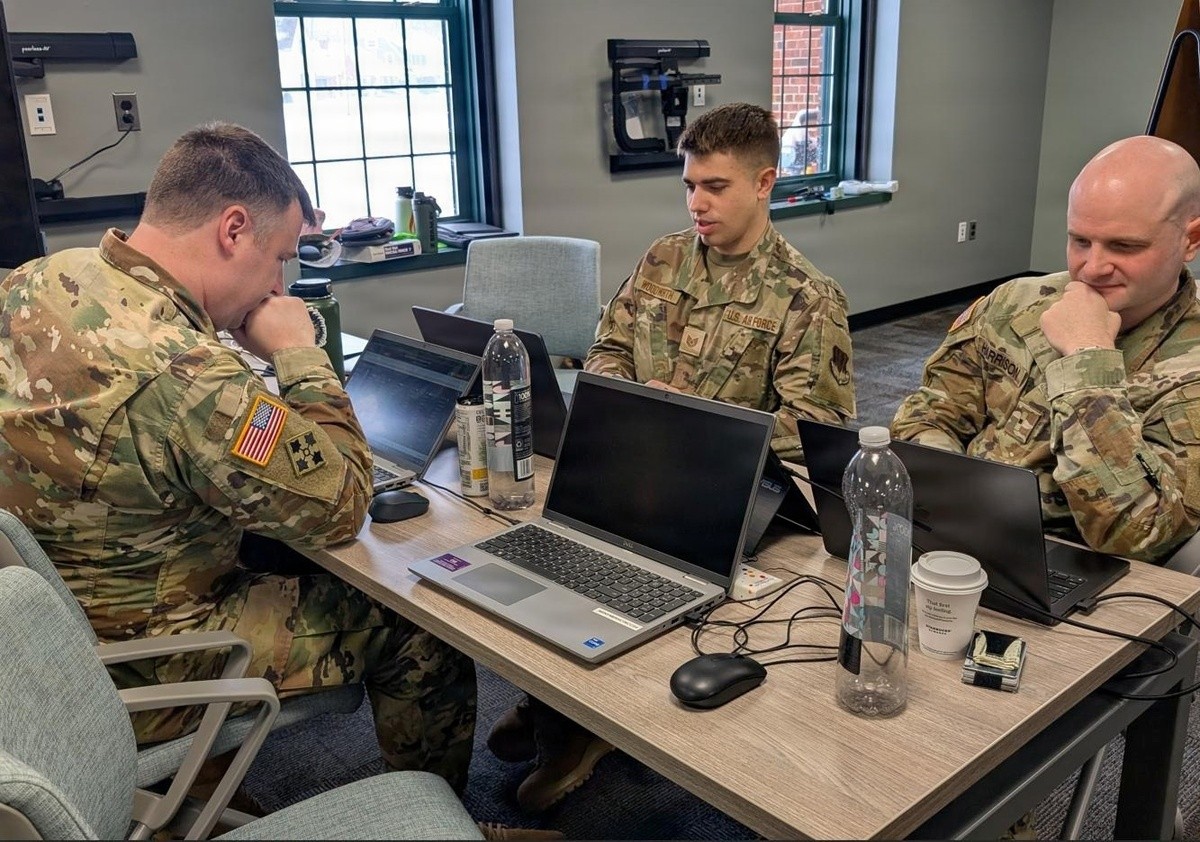
From February 23 to 26, 2026, the New York Army National Guard's Cyber Protection Team 173 engaged in a simulated cyber defense exercise at the Kingston Armory. The exercise involved defending against a simulated threat actor executing a blended cyber operation targeting an electrical utility. The Soldiers utilized the U.S. Cyber Command’s Persistent Cyber Training Environment to replicate real-world cyber challenges. Attackers conducted reconnaissance to identify security weaknesses and executed credential harvesting to gain unauthorized access to systems. The mission for CPT 173 included identifying the breach, closing vulnerabilities, and eliminating malware, specifically ransomware. Thirty-four Soldiers participated in the exercise, which highlighted the importance of cybersecurity for critical infrastructure. The FBI reported significant ransomware attempts in 2024, emphasizing the ongoing threat to utilities and healthcare organizations. Members of CPT 173 leverage their civilian cybersecurity expertise to enhance their military mission.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…