 404Media.Co
Oklahoma Judge Rules Flock ALPR Searches Unconstitutional
Article Content

- •Federal judge ruled Flock ALPR searches unconstitutional due to Fourth Amendment violations.
- •Ruling influenced by Supreme Court's geofencing decision, emphasizing need for warrants.
- •Case involved significant drug evidence but was dismissed due to lack of probable cause.
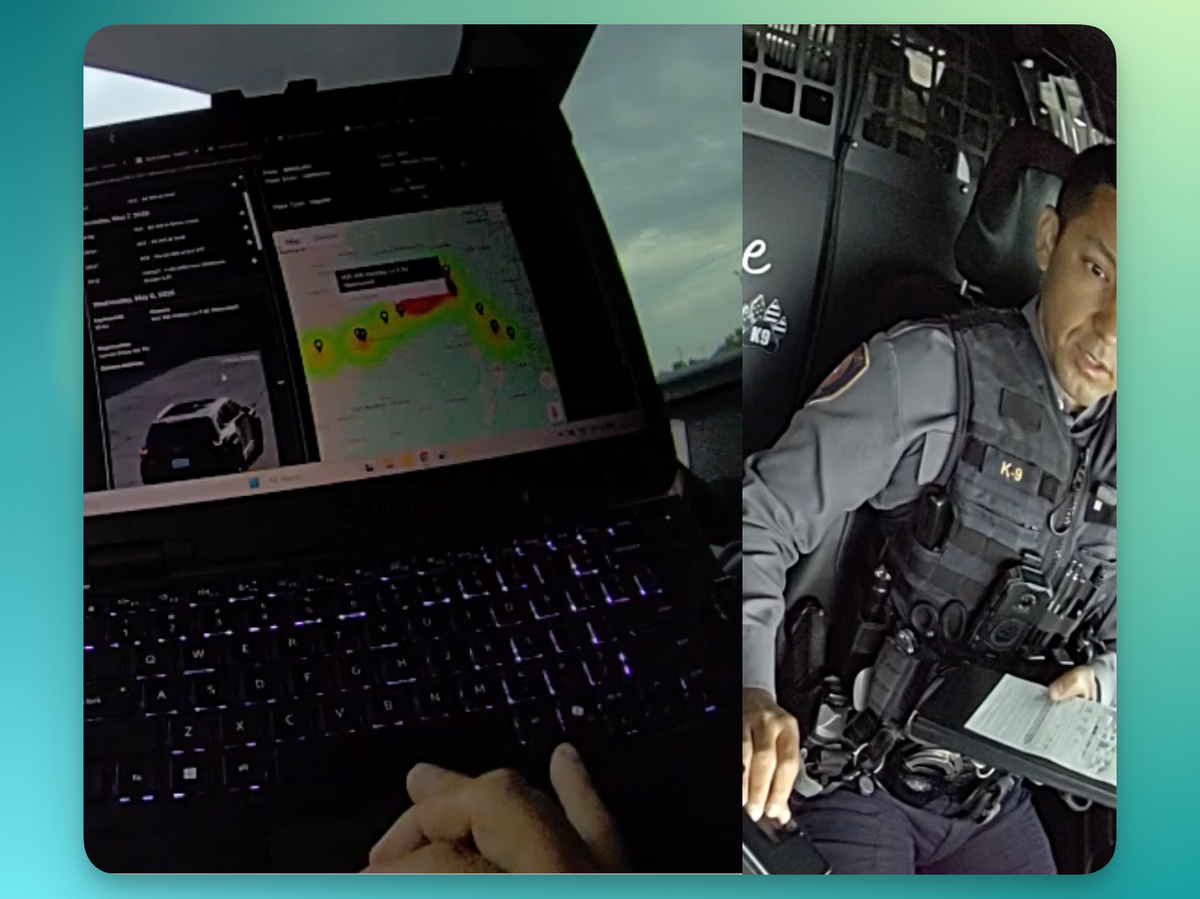
A federal judge in Oklahoma ruled that the use of Flock's automatic license plate recognition (ALPR) system in a meth trafficking case violated the Fourth Amendment. Judge Sara Hill determined that the warrantless search of Melisa Kyle's vehicle history constituted 'indiscriminate mass surveillance.' The ruling, influenced by a recent Supreme Court decision on geofencing, found that ALPR data collection without probable cause is unconstitutional. The judge emphasized that such searches approach a dragnet law enforcement practice and require a warrant. This decision marks a significant shift in legal precedent regarding ALPR data, which has previously been accepted without warrant requirements. The ruling does not create binding precedent but may influence future cases involving digital evidence and privacy rights.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Flock in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the basis for the judge's ruling?
How does this ruling affect future ALPR cases?
What evidence was involved in this case?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…