 Cybermagazine
OpenSSL Faces AI-Driven Bug Surge Amid Cryptography Panel Insights
Article Content

- •OpenSSL has resolved over 600 code issues in the past year with AI assistance.
- •AI-generated security reports complicate the assessment process for maintainers.
- •Experts recommend using AI as a supportive tool rather than for automated coding.
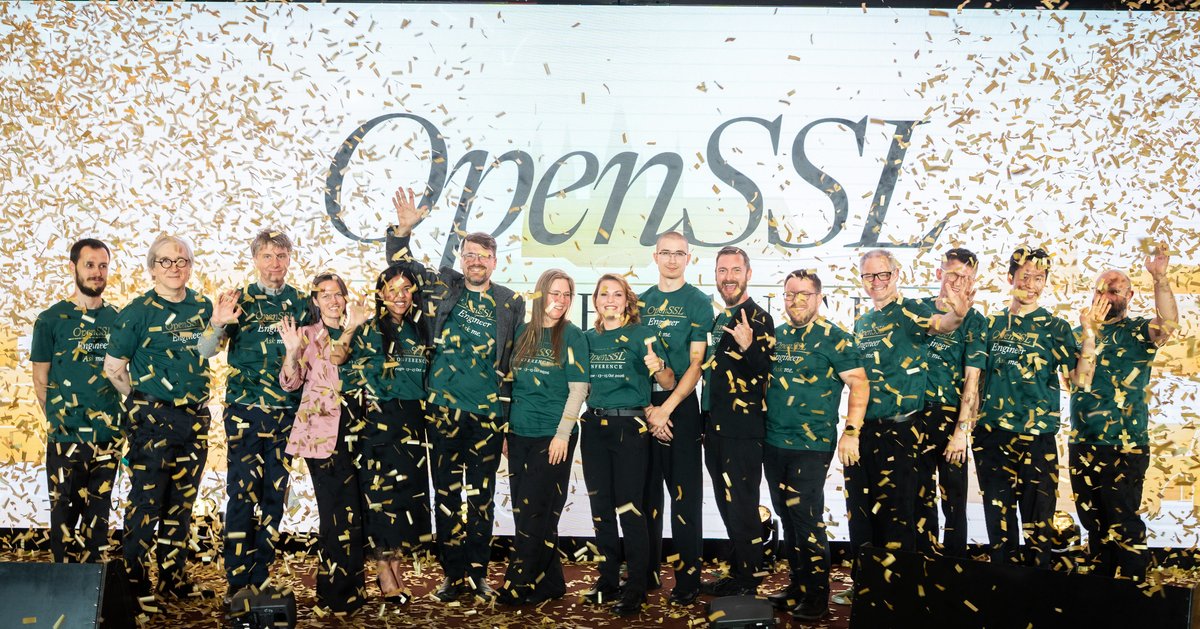
During the OpenSSL Conference 2026 in Prague, experts discussed the impact of AI on open-source cryptography. OpenSSL has addressed over 600 long-standing code issues in the past year, aided by the Sovereign Tech Agency. However, the influx of AI-generated security reports complicates assessment, as many reports are duplicates. Matt Caswell, Executive Director of the OpenSSL Foundation, noted that while AI accelerates problem discovery, it does not increase the number of experienced engineers to evaluate these issues. The community faces a growing challenge as AI tools generate numerous reports, not all of which escalate to CVEs. The panelists emphasized using AI as an assistive technology rather than a replacement for human oversight in code audits and development.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track OpenSSL Corporation in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How many code issues has OpenSSL resolved?
What is the role of AI in the OpenSSL project?
What challenges do maintainers face with AI-generated reports?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…