 Feeds.Feedburner
Operation Endgame Dismantles 1,025 Servers Linked to Major Malware
Article Content
Browse articles 
Europol-led Operation Endgame has successfully seized 1,025 servers associated with the Rhadamanthys, VenomRAT, and Elysium malware. The operation also resulted in the arrest of a key suspect in Greece, disrupting significant global cybercrime activities.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
More articles in this cluster (4)
Following this threat?
Track Elysium in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
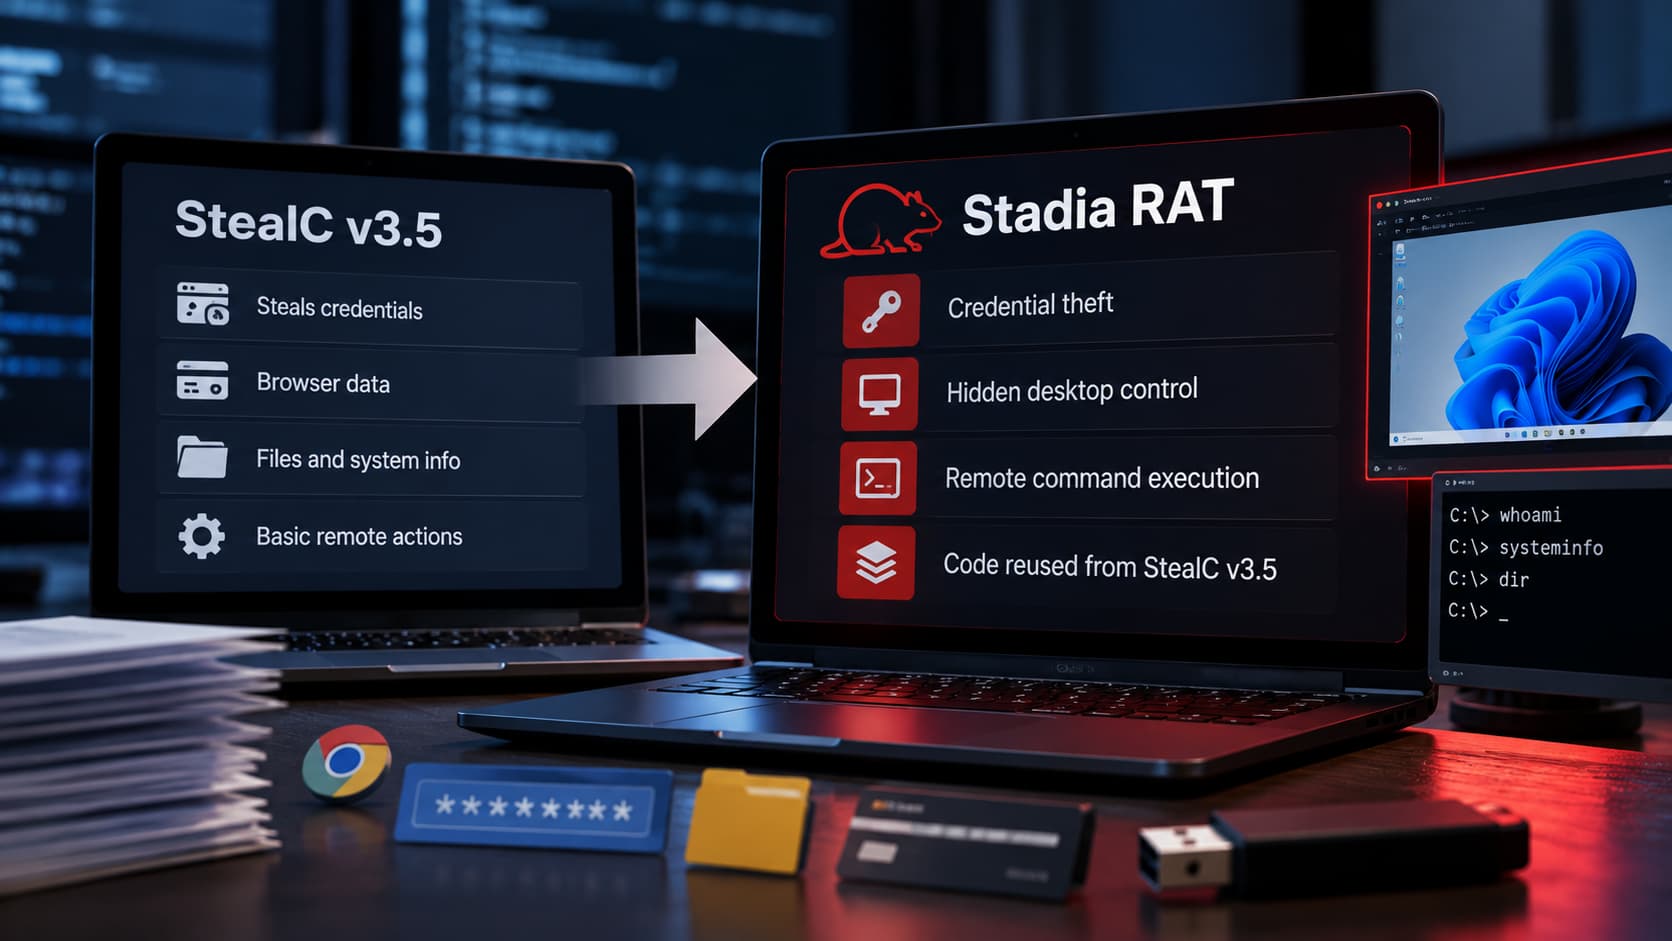 StealC Malware Revives as Stadia RAT with Enhanced Capabilities Following the takedown of StealC by Europol in June 2026, its seller has re-emerged with a new remote access trojan (RAT) named Stadia. This RAT combines credential theft with remote desktop control and command execution, utilizing code from StealC v3.5. Stadia was advertised on October 16, 2026, and features six…
 Cybercriminals Target French Retail with Disruptive Attacks Cybercriminals have overridden temperature settings in hundreds of stores across France, causing fridges to heat up to 50°C and spoiling millions of euros worth of food. This incident highlights a growing trend where cybercriminals pursue business disruption alongside financial gain. The World Economic Forum's Global…