 mwi.westpoint.edu
Operation Vivaldi: Ukraine's Tactical Drone Offensive Reverses Russian Gains
Article Content

- •Operation Vivaldi reversed over a year of Russian territorial gains in eastern Ukraine.
- •Ukrainian forces achieved drone dominance, disrupting Russian logistics and isolating units.
- •The operation forced the elite Rubicon drone unit to retreat, inflicting heavy losses.
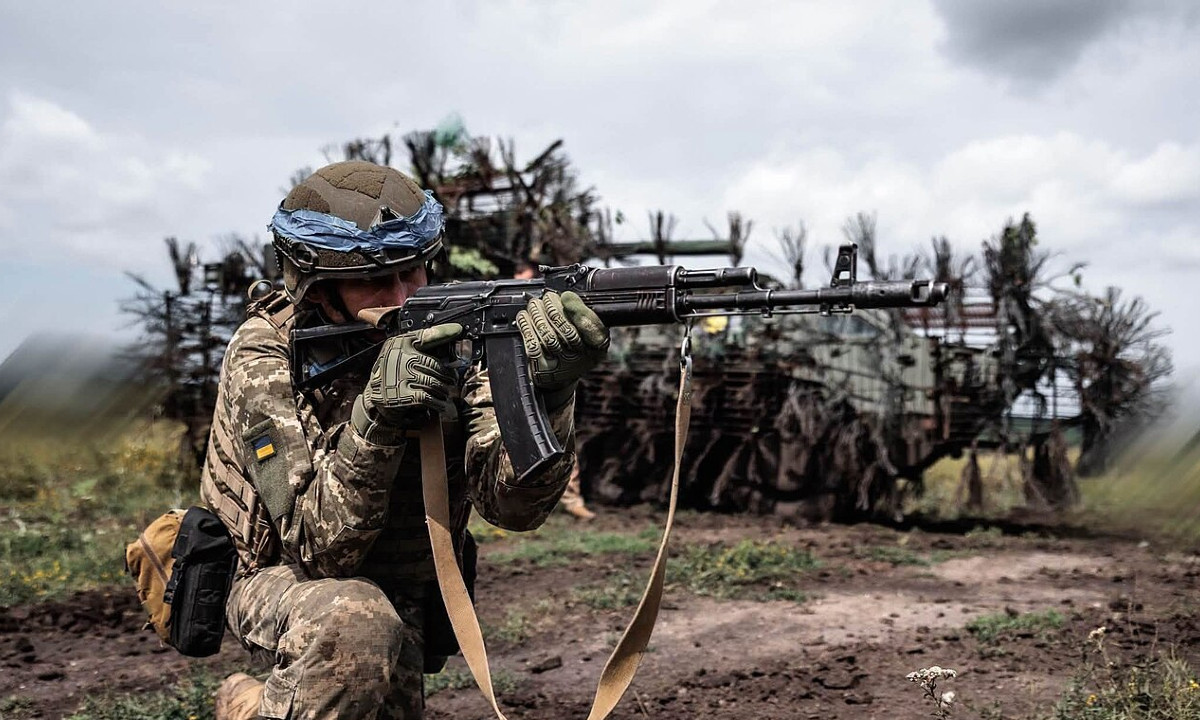
In September 2026, Ukraine launched Operation Vivaldi, a counteroffensive that successfully reversed over a year of Russian territorial gains in the Lyman sector of eastern Ukraine. This operation showcased Ukraine's tactical innovations, particularly in drone warfare, as Ukrainian forces achieved drone dominance over Russian units. Reports indicate that Ukraine's 3rd Corps, supported by two brigades from the Unmanned Systems Forces, utilized drones to disrupt Russian logistics and isolate their forces. Ukrainian commanders created an electronic warfare 'curtain' to conceal movements and prevent Russian reconnaissance. The offensive resulted in the retreat of Russia's elite Rubicon drone unit, with significant losses reported in logistics and personnel. The operation has been characterized as a decisive battlefield victory that may alter Russia's strategic calculations in the ongoing conflict. The success of Operation Vivaldi highlights the evolving nature of combat operations in an era increasingly defined by drone warfare.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…