 optics11.com
Optics11 Secures €50 Million for Fiber Optic Sensing Amid Rising Security Threats
Article Content

- •Optics11 raised €50 million to scale its fiber optic sensing technology.
- •Total investment in Optics11 exceeds €100 million in just 15 months.
- •The technology is crucial for enhancing security in response to hybrid warfare and energy demands.
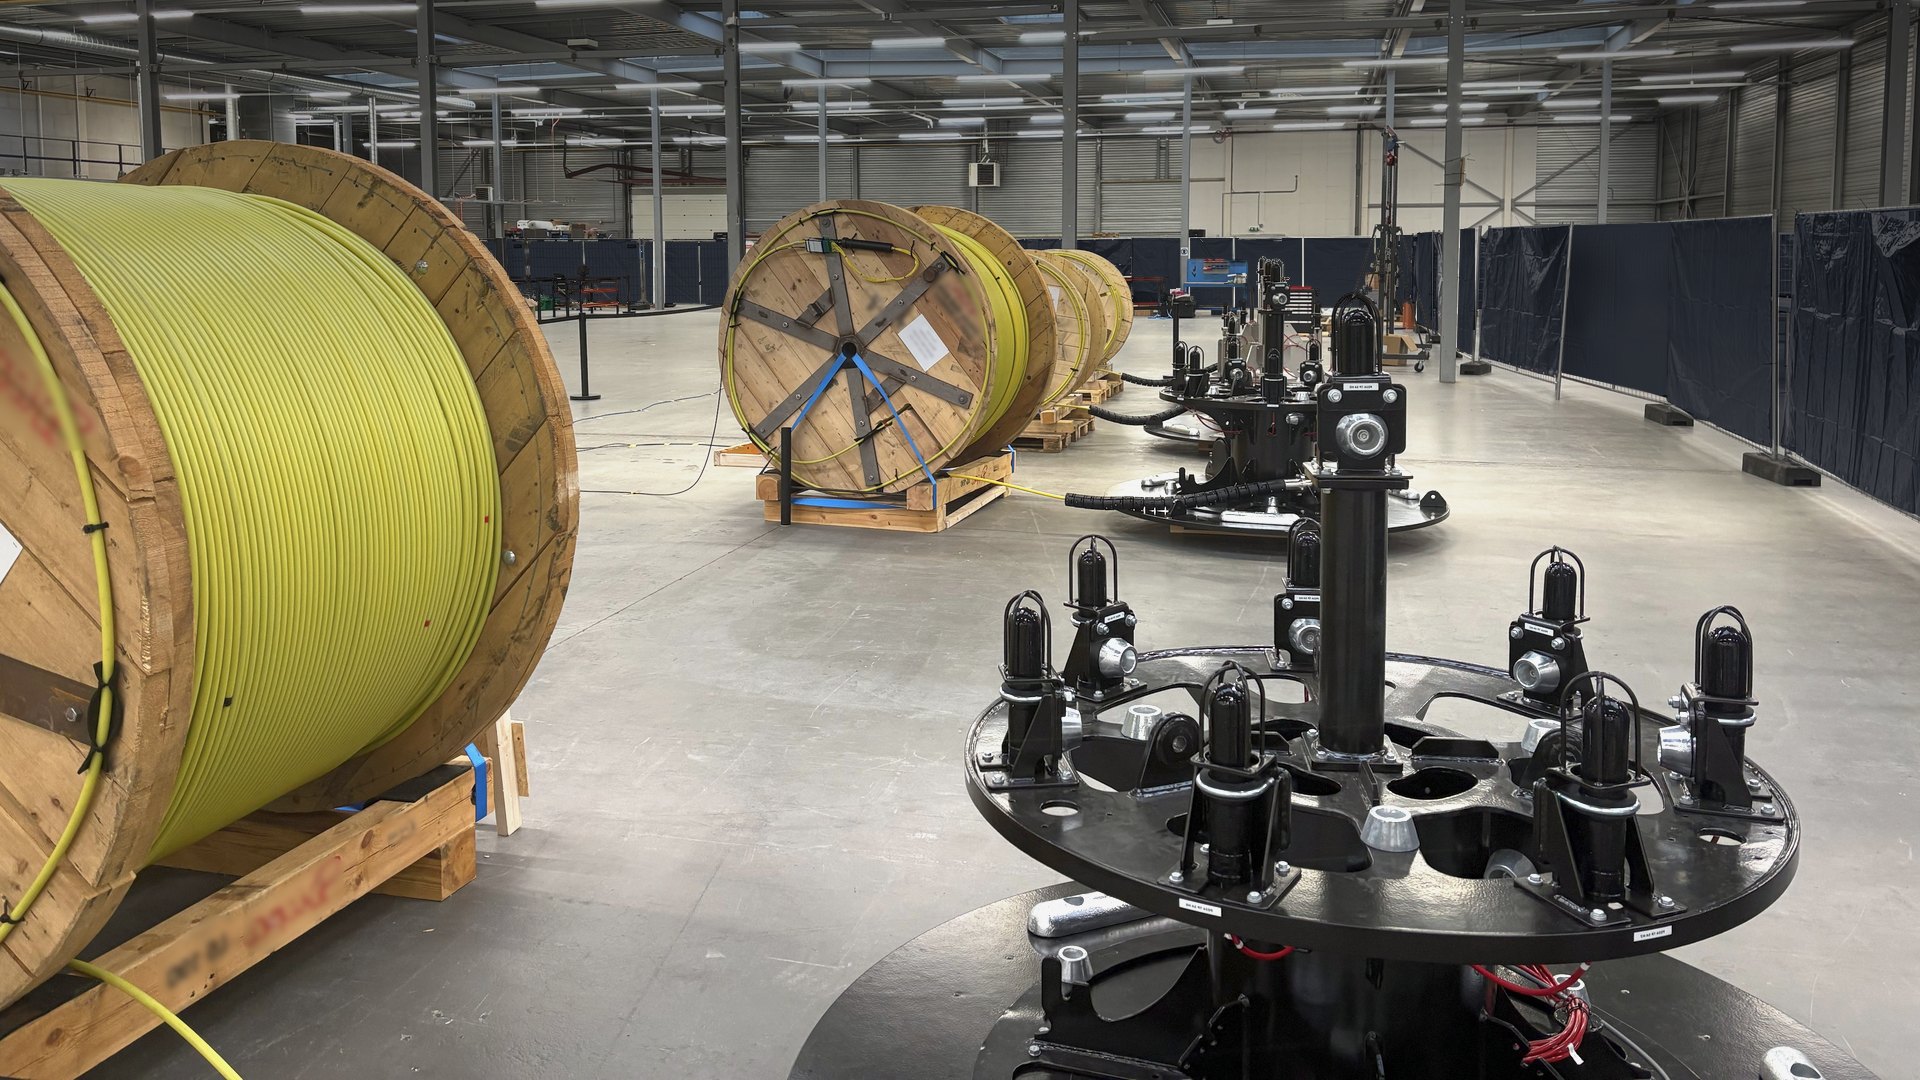
Optics11, a Dutch company specializing in fiber optic sensing technology, announced a €50 million investment to enhance its manufacturing and international expansion capabilities. This funding, backed by existing investors, brings total investment to over €100 million in 15 months, driven by escalating hybrid warfare threats and the need for energy grid resilience in Europe. The investment aims to meet growing global demand for advanced sensing technologies that protect critical infrastructure. Optics11's technology, which captures acoustic signals using light, offers advantages over traditional sensing methods, making it appealing for underwater intelligence and energy grid monitoring. The Dutch Ministry of Defence has already selected Optics11's technology for its Anti-Submarine Warfare program, highlighting its significance in enhancing maritime surveillance capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Optics11 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is Optics11's technology used for?
Who are the investors in this funding round?
What is the significance of this investment?
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical RCE and LPE Vulnerabilities in Quest Foglight for Databases On November 3, 2026, the Zero Day Initiative disclosed multiple critical vulnerabilities in Quest Foglight for Databases, including six remote code execution (RCE) flaws and two local privilege escalation (LPE) vulnerabilities. The most severe RCE vulnerabilities, CVE-2026-92189 and CVE-2026-92190, allow…