 Pakistantoday.Pk
Pakistan Calls for UN Action Against Disinformation Amid Global Conflicts
Article Content

- •Pakistan urges the UN to address the growing threat of disinformation and hate speech.
- •Ambassador Jadoon emphasizes the impact of false narratives on human rights in conflict zones.
- •Technological advancements have both democratized information and accelerated misinformation spread.
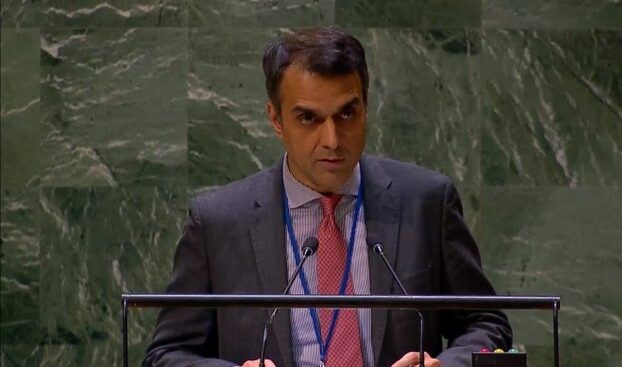
On April 29, 2026, Pakistan's Deputy Permanent Representative to the UN, Usman Jadoon, addressed the UN Committee on Information, urging the organization to combat the rising tide of disinformation and hate speech that are exacerbating global conflicts. He highlighted the detrimental effects of false narratives on human rights, particularly in regions like Palestine and Kashmir, where such misinformation obscures realities and suppresses legitimate voices. Jadoon emphasized the need for timely and accurate communication in an increasingly polarized world, warning that the misuse of digital platforms is deepening social divisions and targeting vulnerable communities. He pointed out that advancements in technology, while democratizing information access, have also accelerated the spread of misinformation and hate speech. The envoy called for a comprehensive and balanced response to these challenges, particularly in light of the rise of artificial intelligence and generative technologies, which pose new risks to information integrity.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…