 Kabulnow
Pakistan Conducts Airstrikes in Afghanistan Amid Rising Tensions
Article Content

- •Pakistan's airstrikes in Afghanistan are claimed to target militants but result in civilian casualties.
- •The Taliban denies Pakistan's accusations of harboring terrorists and condemns the airstrikes as violations of sovereignty.
- •The UN reports confirmed civilian casualties, highlighting the humanitarian impact of the conflict.
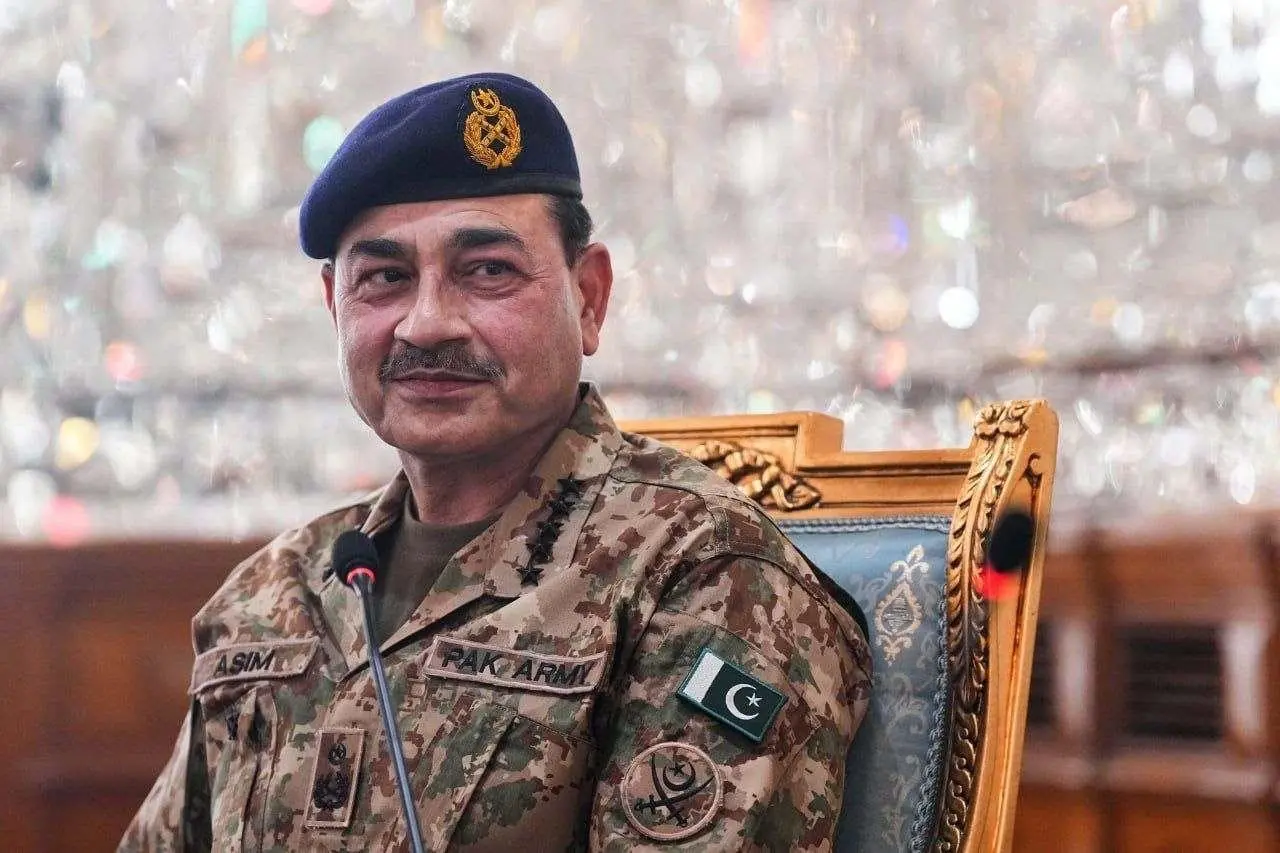
On October 1, 2026, Pakistan conducted airstrikes in Afghanistan's Kunar and Helmand provinces, claiming to target militant hideouts. Pakistan's military reported killing 22 militants, while Afghan authorities reported civilian casualties, including nine deaths and injuries to 11 others. The airstrikes followed previous attacks on September 21, where three civilians were killed. Pakistan's Army Chief Asim Munir justified the actions as counterterrorism operations, blaming the Taliban for allowing militant groups to operate from Afghan territory. The United Nations confirmed civilian casualties and called for de-escalation. Tensions between Pakistan and the Taliban have escalated, with both sides accusing each other of violating sovereignty and facilitating terrorism. The situation remains volatile, with ongoing military confrontations reported.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What were the reported civilian casualties?
What justification did Pakistan provide for the airstrikes?
How has the international community responded?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…