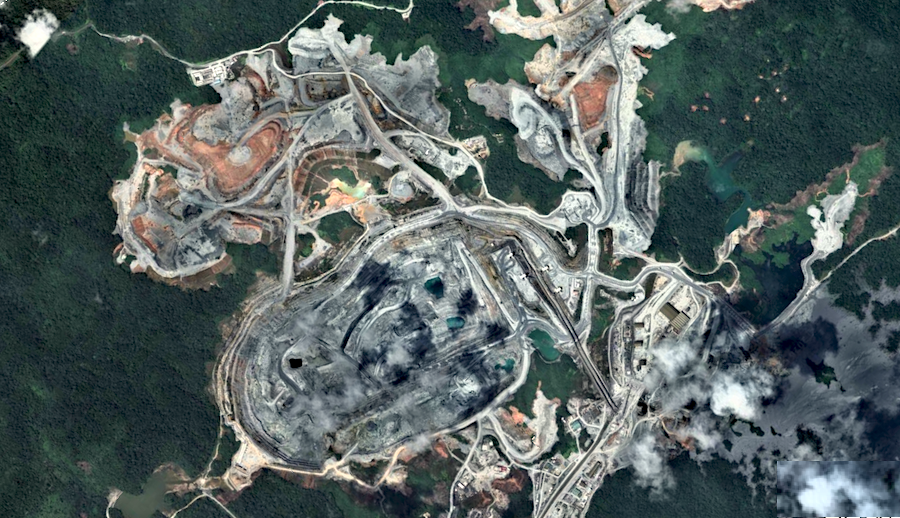
 Mining
Panama Commission Recommends Orderly Closure of Cobre Panama Mine
Article Content

- •Panama's commission recommends an orderly closure of the Cobre Panama mine.
- •The mine's closure has led to significant job losses and reduced state revenue.
- •First Quantum's shares dropped 31% following the announcement of the commission's proposal.
A Panamanian government commission has recommended President José Raúl Mulino to order the final closure of First Quantum Minerals’ Cobre Panama mine. This recommendation follows an independent audit that evaluated the mine's economic, environmental, and legal implications. The commission suggests negotiating a new arrangement to allow a temporary restart of operations to facilitate an orderly closure without financial burden on the state. The mine, which produced up to 1.5% of global copper, was shut down in 2023 due to protests over environmental concerns. The closure resulted in the loss of approximately 36,000 jobs and a significant reduction in state revenue. The commission's proposal is not final and requires the president's decision. First Quantum has not yet commented on the recommendation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track First Quantum Minerals in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the implications of the mine's closure?
What is the current status of First Quantum's operations?
What will the government do next?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…