 Khpg
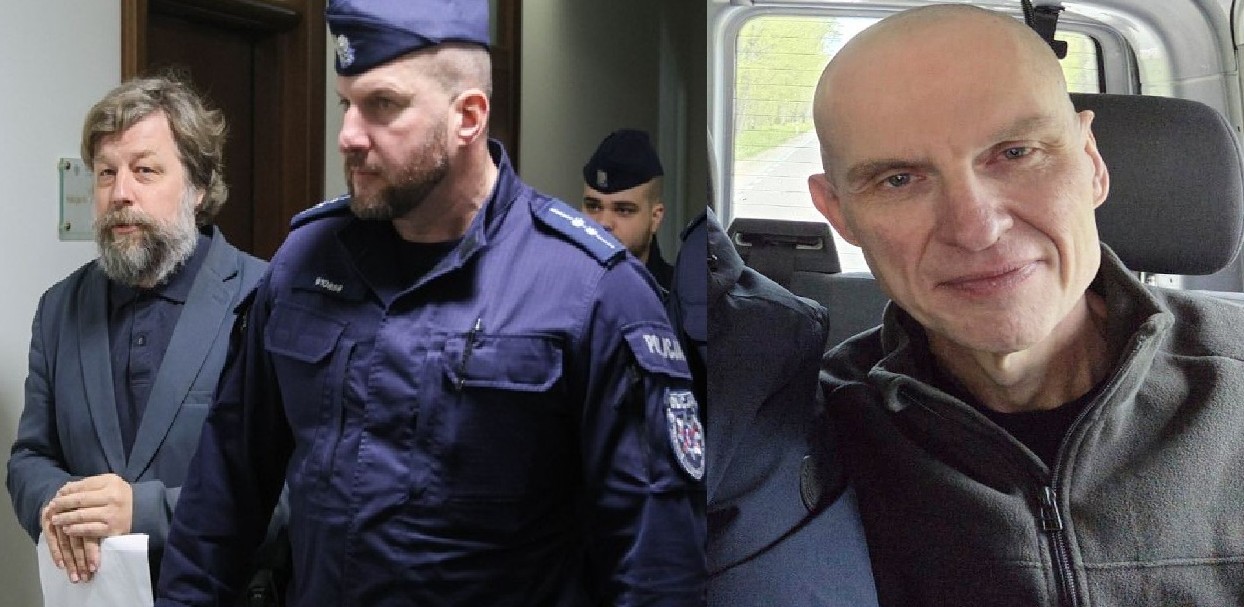
Prisoner Exchange Involves Controversial Russian Archaeologist and Journalist Release
Article Content

- •Andrzej Poczobut was released after nearly five years in Belarusian custody.
- •Alexander Butyagin, wanted by Ukraine, was returned to Russia despite extradition proceedings.
- •The exchange reflects significant geopolitical maneuvering involving Belarus, Poland, and Russia.
On April 28, 2026, a significant prisoner exchange occurred at the Polish-Belarusian border, involving five individuals from each side. Notably, Polish journalist Andrzej Poczobut was released after being imprisoned since March 2021, while Russian archaeologist Alexander Butyagin was returned to Russia despite facing extradition to Ukraine for illegal activities in occupied Crimea. The exchange highlights the geopolitical tensions involving Belarus, Poland, and Ukraine, with implications of Russian influence over Belarusian decisions. The exchange included individuals accused of espionage and treason, raising concerns about the motivations behind the swap. The involvement of the U.S. administration in the negotiations remains unclear, leading to frustrations in Ukraine regarding their exclusion from the deal. This event underscores the complex interplay of international relations and intelligence operations in Eastern Europe.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…