 Channelnewsasia
Putin and Iran's Pezeshkian Discuss Ending US-Led Conflict in the Middle East
Article Content

- •Putin pledged full support to Iran in ending the US-led conflict.
- •The meeting highlights the growing military and diplomatic ties between Russia and Iran.
- •Iran-US negotiations are reportedly at a standstill, complicating conflict resolution.
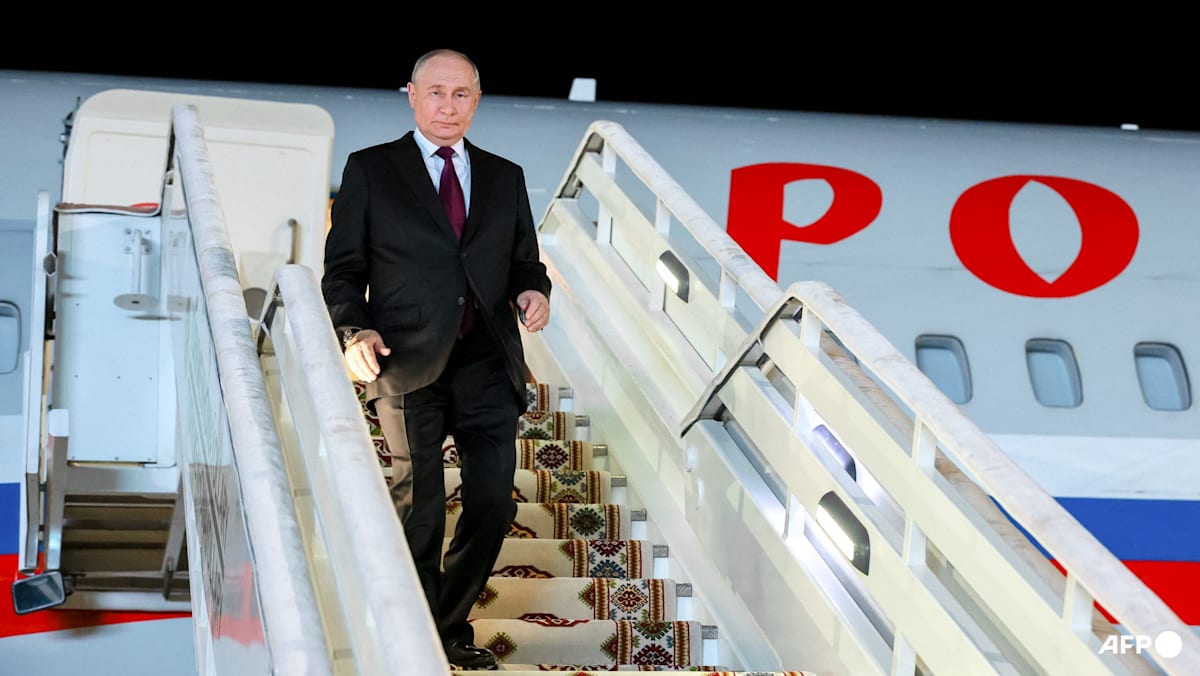
On October 8, 2026, Russian President Vladimir Putin met with Iranian President Masoud Pezeshkian in Turkmenistan, pledging Russia's support to help end the ongoing US-led war on Iran. Putin stated that Russia would 'do everything' to assist in resolving the conflict, which he claimed Iran did not initiate. The meeting occurred ahead of a Commonwealth of Independent States summit and follows a history of strengthened diplomatic and military ties between Russia and Iran. Both leaders acknowledged the impasse in Iran-US negotiations, with Pezeshkian describing talks with Washington as 'meaningless.' Putin also expressed readiness to mediate in the conflict. The discussions come amid accusations against Iran for supplying drones to Russia for its Ukraine offensive, while Russia has been accused of providing intelligence to Iran for attacks on US targets in the Middle East.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What was discussed in the meeting?
What is the current status of US-Iran negotiations?
How does this affect Russia-Iran relations?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…