 Independent
RAF Gunners Achieve 'Ace' Status by Neutralizing Iranian Drones
Article Content

- •RAF gunners became the first drone 'aces' by shooting down five Iranian drones.
- •The Rapid Sentry air defense system is crucial for intercepting threats in the region.
- •The UK plans to bolster its air defense by deploying more systems and acquiring additional missiles.
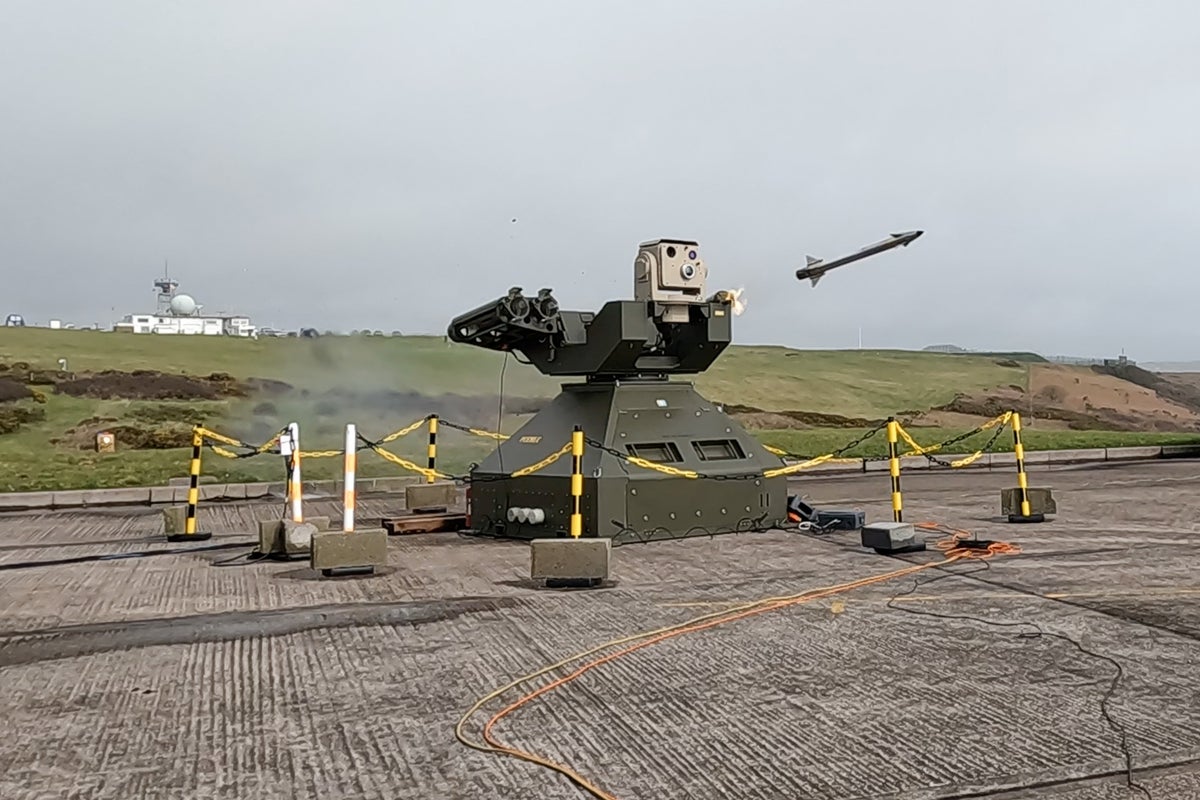
For the first time in history, RAF Regiment gunners have achieved the title of drone 'aces' by successfully shooting down five or more Iranian drones during operations in the Middle East. This recognition aligns with the traditional definition of 'ace' from World War II, where pilots earned the title for downing five enemy aircraft. The gunners are tasked with protecting British bases from threats posed by Iranian drones, particularly the Shahed models. Their operations have intensified since the onset of the American-Israeli war with Iran in late February 2026. The RAF Regiment employs advanced tools such as early-warning sensors, electronic warfare systems, and the Rapid Sentry air defense system, which is armed with Lightweight Multirole Missiles (LMM). The British government plans to enhance its air defense capabilities by deploying the Rapid Sentry system to Kuwait and acquiring additional missiles. Minister Al Carns and Air Commodore Paul Hamilton have publicly praised the gunners for their professionalism and bravery in high-pressure conditions. The recent achievements highlight the evolving nature of air defense in modern warfare.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…