 Bhaskarenglish.In
Rajasthan Intelligence Dismantles Espionage Network; IAF Staffer Arrested
Article Content

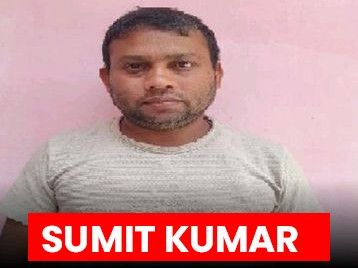
- •Sumit Kumar, a civilian IAF employee, was arrested for espionage linked to Pakistan.
- •He allegedly leaked sensitive military information via social media in exchange for payments.
- •The operation revealed a broader espionage network targeting Indian defense installations.
Rajasthan Intelligence has arrested Sumit Kumar, a 36-year-old civilian employee at the Chabua Air Force Station in Assam, for allegedly leaking sensitive information to Pakistani intelligence handlers. The operation, which began in January 2026, followed the earlier arrest of Jhabara Ram, who initially provided leads on Kumar's involvement. Kumar reportedly misused his position to gather confidential data about the Indian Air Force, including locations of fighter aircraft and missile systems, and transmitted this information via social media in exchange for money. The joint operation with Air Force Intelligence led to his detention on March 22, 2026, and he is now being interrogated in Jaipur. A case has been registered under the Official Secrets Act and the Bharatiya Nyaya Sanhita Act. Authorities believe this arrest has exposed a broader espionage network targeting Indian defense infrastructure. Further investigations are ongoing to identify additional collaborators.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Chabua Air Force Station in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…