 www.prnewswire.com
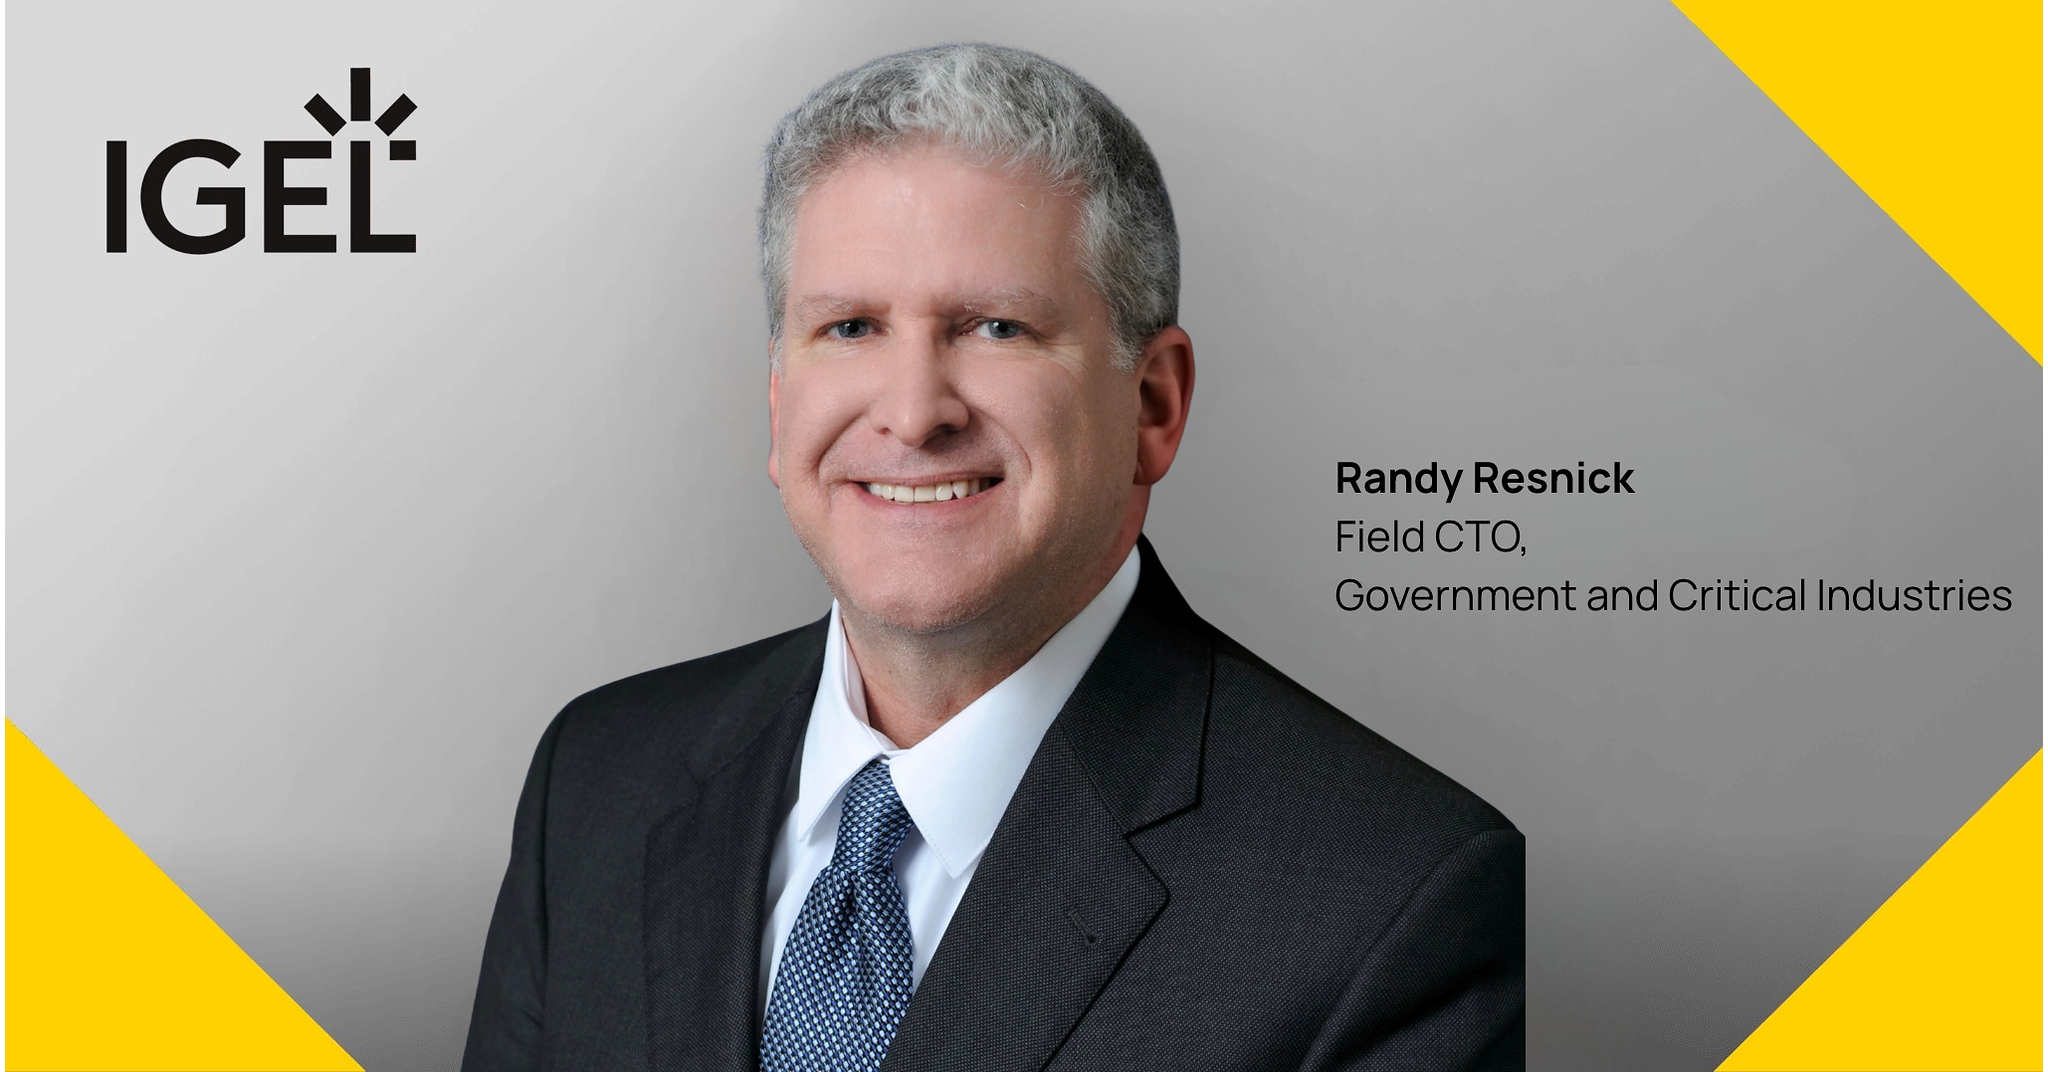
Randy Resnick Joins IGEL to Enhance Zero Trust Strategy
Article Content

- •Randy Resnick joins IGEL as Field CTO to enhance Zero Trust initiatives.
- •Resnick has extensive experience from the DoD and NSA, focusing on cybersecurity.
- •IGEL aims to apply national security frameworks to commercial critical infrastructure.
Randy Resnick, a prominent figure in Zero Trust cybersecurity, has been appointed as Field CTO at IGEL, a global software company. With nearly 40 years of experience at the DoD and NSA, Resnick aims to advance the IGEL Adaptive Secure Endpoint Platform (IASEP) focusing on Zero Trust, cyber resilience, and AI across government and critical industries. His previous role involved leading the DoD's Zero Trust strategy, which he helped transform into a national defense framework. Resnick's expertise will help IGEL translate national security-grade frameworks into commercial applications for sectors like healthcare, finance, and energy. This strategic move is seen as a validation of IGEL's platform approach to cybersecurity. Resnick's mission will extend internationally, impacting NATO and Five Eyes countries, as well as Japan and South Korea.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Department of Defense in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is Randy Resnick's background?
What is the focus of IGEL's Adaptive Secure Endpoint Platform?
How will Resnick's role impact IGEL's strategy?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…