 Pasqualepillitteri.It
Ransomware Tracking and Data Breaches in France and Europe
Article Content

- •Cyberattaque.org reports on ongoing data breaches in France, emphasizing the need for verification.
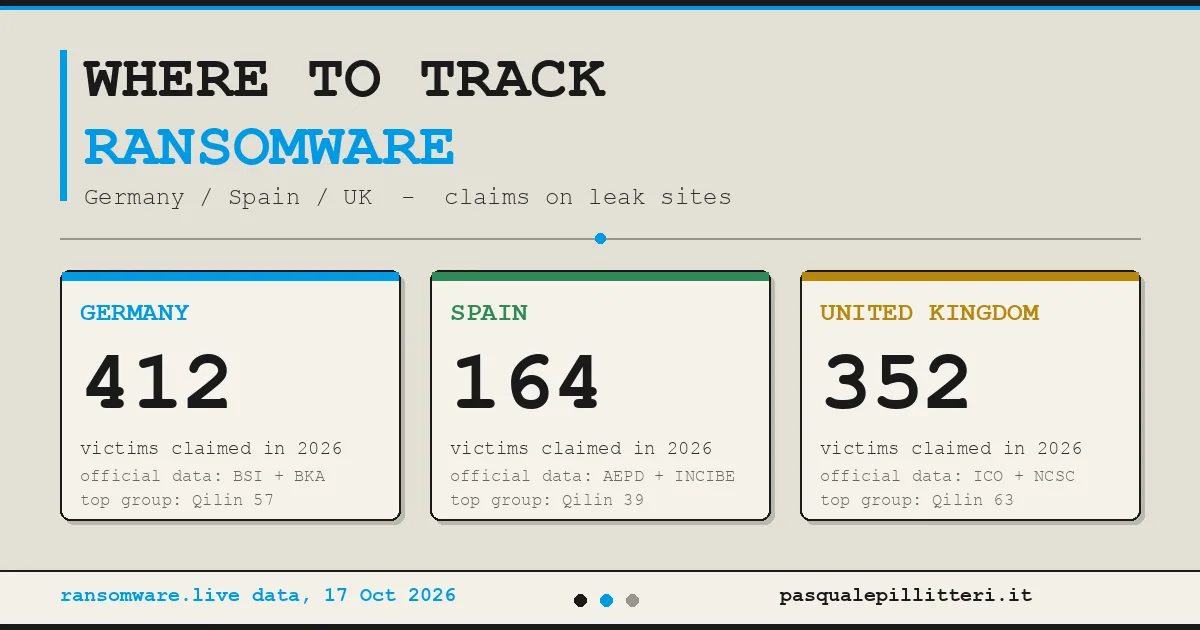
- •Ransomware incidents in Germany, Spain, and the UK have surged in 2026, with notable increases in victim counts.
- •Both platforms highlight the importance of distinguishing between confirmed incidents and claims by hackers.
Cyberattaque.org, a French site, reports on multiple data leaks and cyberattacks affecting various sectors, including companies and political parties. The site, launched in March 2026, serves as an independent observatory but lacks verified sources and methods. It distinguishes between confirmed data leaks and claims made by hackers. Meanwhile, ransomware.live tracks ransomware incidents in Germany, Spain, and the UK, reporting significant increases in victims in 2026 compared to 2025. The site lists 412 victims in Germany, 352 in the UK, and 164 in Spain as of October 17, 2026. The data is sourced from criminal gang claims, police reports, and data protection authorities, but discrepancies exist among these sources. Both platforms emphasize the need for verification and caution in interpreting their data.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Following this threat?
Track DragonForce and Afflelou in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of organizations are affected?
How reliable is the data from Cyberattaque.org?
What is the current status of ransomware incidents in Europe?
Continue Reading
 Emerging EDR Killer Tool Targeting Ransomware Groups A new malicious tool, referred to as the EDR killer, is being actively used by at least eight ransomware groups, including Blacksuit and Medusa, to disable endpoint detection and response (EDR) solutions. This tool is believed to be an evolution of the EDRKillShifter developed by RansomHub, which allows ransomware…
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…