 Businesstimes.Sg
Rising Cyber Insurance Demand in Singapore Amid Increasing Phishing Threats
Article Content

- •Cyber insurance demand is rising in Singapore due to increased phishing threats.
- •UEI Logistics experienced a phishing scam that led to the purchase of cyber insurance.
- •Premiums for cyber insurance have fallen, making coverage more accessible.
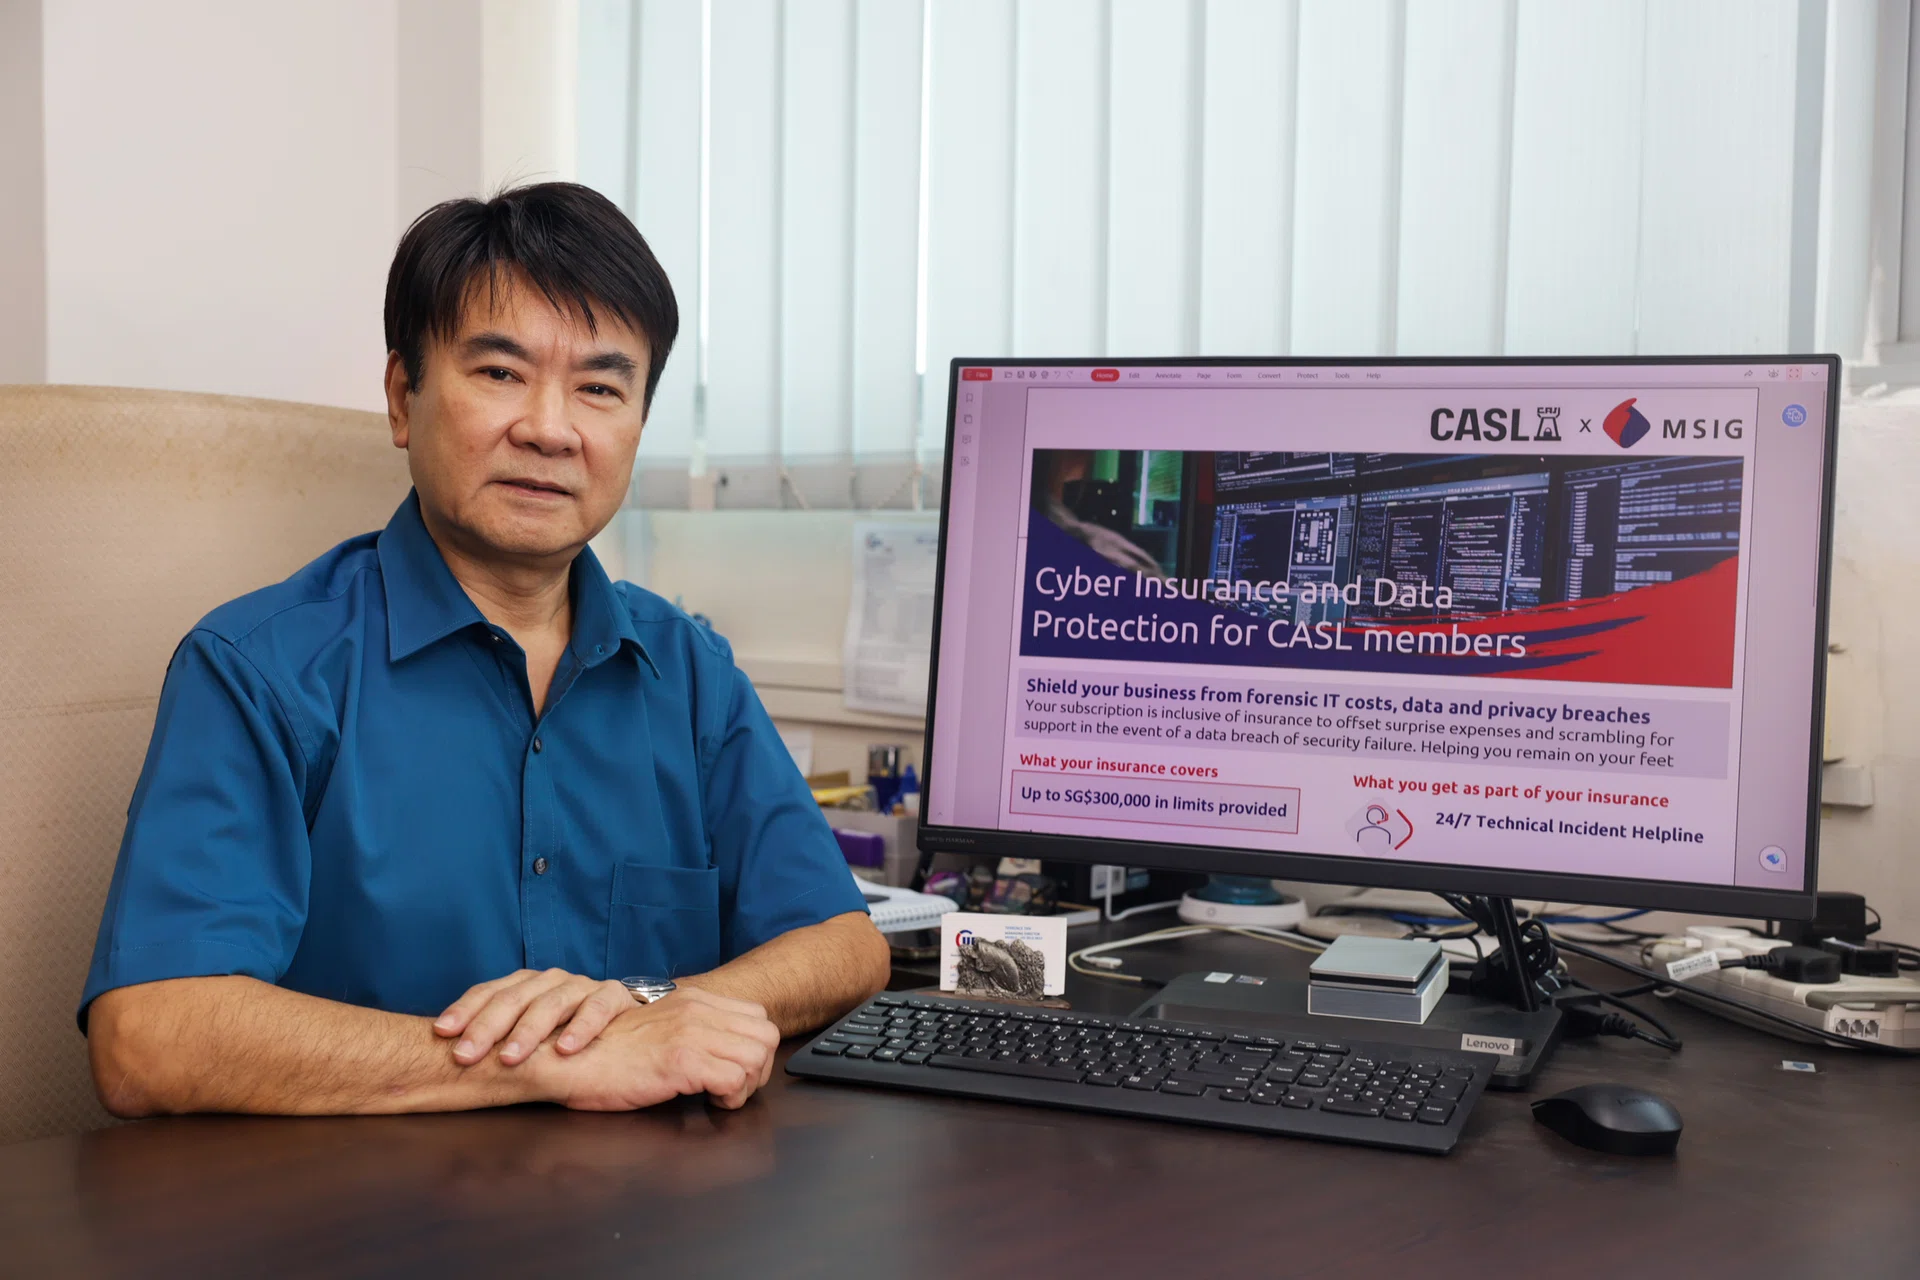
In Singapore, the demand for cyber insurance is on the rise as companies face increasing phishing threats. UEI Logistics, a freight forwarding company, experienced a phishing scam in November 2025, where attackers impersonated a trusted partner to request a large payment. This incident prompted UEI Logistics to implement a threat detection system and purchase a cyber insurance policy from MSIG, providing S$300,000 coverage for various breach-related costs. Insurers report that technology and financial firms are the primary buyers, with growing interest from sectors like manufacturing and healthcare. Since 2022, premiums for cyber insurance have decreased, making it more accessible for small and mid-sized enterprises. Major insurers like Markel and QBE Asia have reported significant increases in policy sales, indicating a broader trend towards cyber risk management in Singapore.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track UEI Logistics in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…