 Lbc
RNLI Data Breach Amid Far-Right Targeting of Charity
Article Content

- •RNLI warns supporters of potential data breach affecting personal information.
- •Cyber-attack targeted Beacon CRM, impacting around 1,500 charities.
- •RNLI volunteers face abuse and protests for aiding migrants at sea.
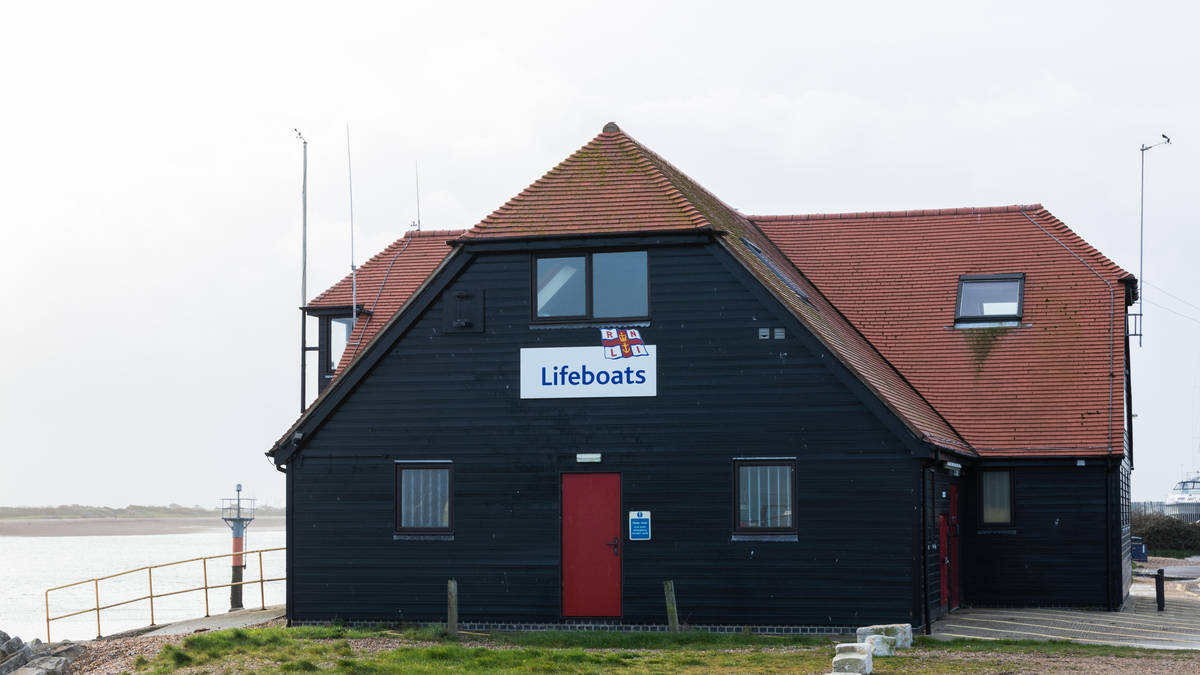
The Royal National Lifeboat Institution (RNLI) has warned supporters that their personal information may have been compromised due to a cyber-attack on Beacon CRM, a company managing its customer data. The breach, which occurred in late July, affects approximately 1,500 charities, with RNLI advising members to assume their names and interaction records were accessed. This incident follows a surge in hostility towards RNLI volunteers, who have faced abuse for assisting migrants at sea. The RNLI's Portsmouth lifeboat station was temporarily closed due to ongoing threats and protests against the charity's actions. Although there is currently no evidence of misuse of the stolen data, the RNLI has advised volunteers to avoid wearing branded clothing to mitigate risks. The charity has reported a significant increase in donations despite the threats. The RNLI's chief executive condemned the abuse directed at volunteers as unacceptable.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track RNLI in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…