 Rferl
Rubio Visits NATO Allies Amid Rising Russian Threats
Article Content

- •Rubio's visit addresses NATO security concerns due to Russian military activities.
- •Iceland's strategic location in the North Atlantic is vital for NATO operations.
- •The agenda includes discussions on defense cooperation and economic collaboration.
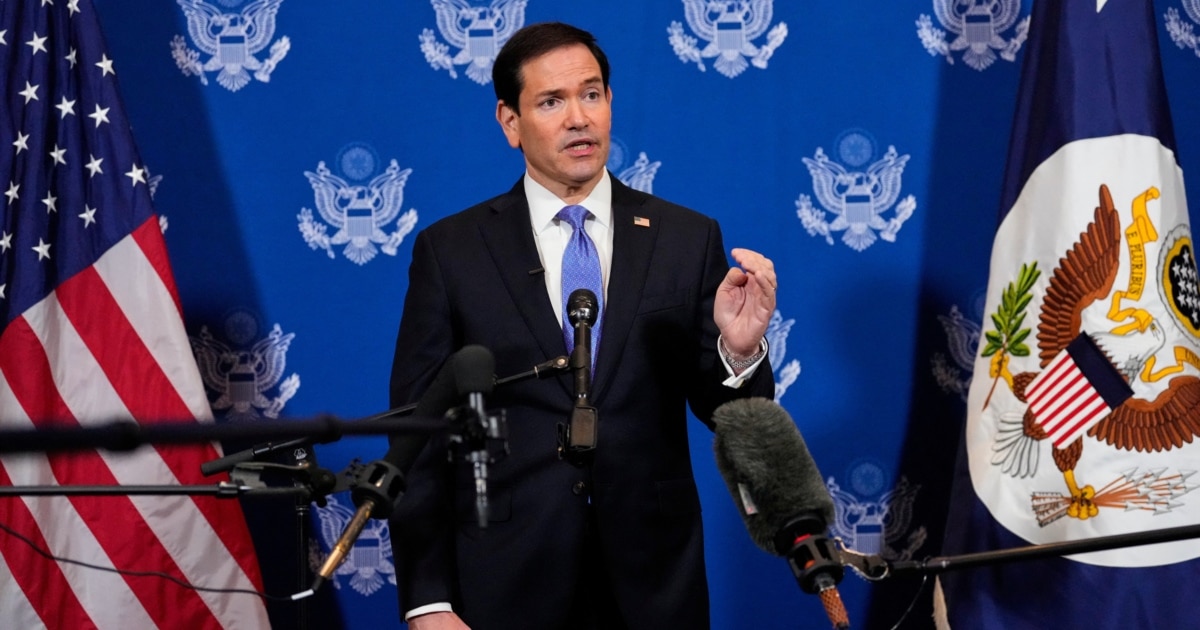
US Secretary of State Marco Rubio is visiting Iceland, Greece, and Portugal from October 5-8, 2026, to discuss security and defense cooperation amid increasing concerns over Russian military activity and instability in the Middle East. In Reykjavik, he will focus on Arctic security and economic cooperation, while in Athens, the agenda includes defense cooperation and regional security in relation to Ukraine and the Middle East. In Lisbon, discussions will center on defense, economic development, and technology cooperation. Iceland, which has no standing army, has cooperated with NATO on security since Russia's annexation of Crimea in 2014. The visit follows commitments made by Arctic countries to enhance their own security and protect critical infrastructure. The discussions are critical as NATO allies face a real threat from Russian military activities in the Arctic region, particularly concerning submarine warfare and the protection of undersea telecommunications cables.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What is the purpose of Rubio's visit?
How does Iceland contribute to NATO?
What are the main topics of discussion during the visit?
Continue Reading
 Critical Zero-Day Exploit in BeyondTrust Remote Support Disclosed BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE. The flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring credentials or user…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…