 Rferl
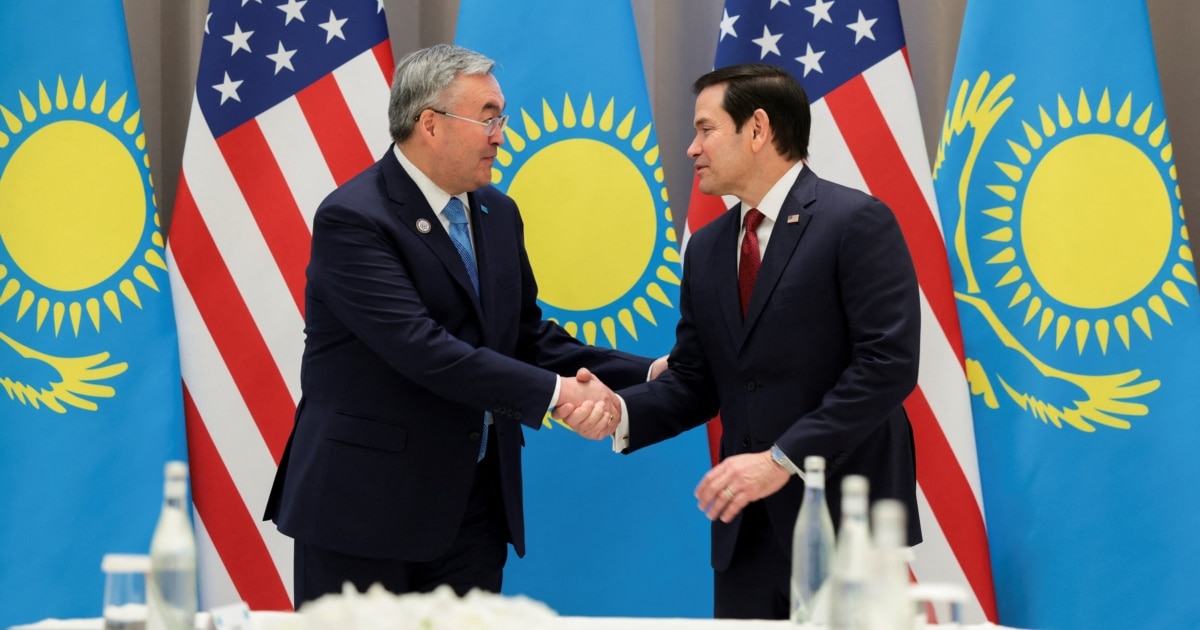
Rubio Warns of Escalation Risks in Ukraine Conflict During Central Asia Visit
Article Content

- •Rubio warns of risks of conflict escalation into neighboring countries.
- •Discussions about a potential peace meeting involving Trump, Putin, and Xi Jinping are ongoing.
- •The U.S. has temporarily suspended some sanctions to encourage negotiations.
On October 19, 2026, U.S. Secretary of State Marco Rubio emphasized the need to end the ongoing war between Ukraine and Russia during his visit to Uzbekistan. He warned of the potential for the conflict to escalate into neighboring countries due to failed sabotage attacks and drone incidents. Rubio mentioned discussions regarding a potential meeting between U.S. President Donald Trump, Russian President Vladimir Putin, and Chinese President Xi Jinping to negotiate peace, although he noted that no final arrangements had been made. He defended the Trump administration's decision to temporarily suspend certain sanctions to facilitate negotiations. The war has resulted in significant casualties, with claims of up to 25,000 deaths per month. Rubio's remarks come amid ongoing violence, including a recent Russian airstrike in Kyiv that killed a civilian and damaged infrastructure.
Ask AI about this cluster
Answers cite the sources they use
More articles in this cluster (2)
Common questions
What is the current status of the Ukraine conflict?
What actions is the U.S. taking regarding sanctions?
What are the implications of the recent airstrike in Kyiv?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…