 Lbc
US Intelligence Warns of Imminent Russian Threats to NATO
Article Content

- •US intelligence warns of potential Russian provocations against NATO within years.
- •Possible attack methods include cyber strikes and small land incursions, particularly targeting Poland.
- •Recent incidents, such as a missile landing in Poland, indicate escalating tensions.
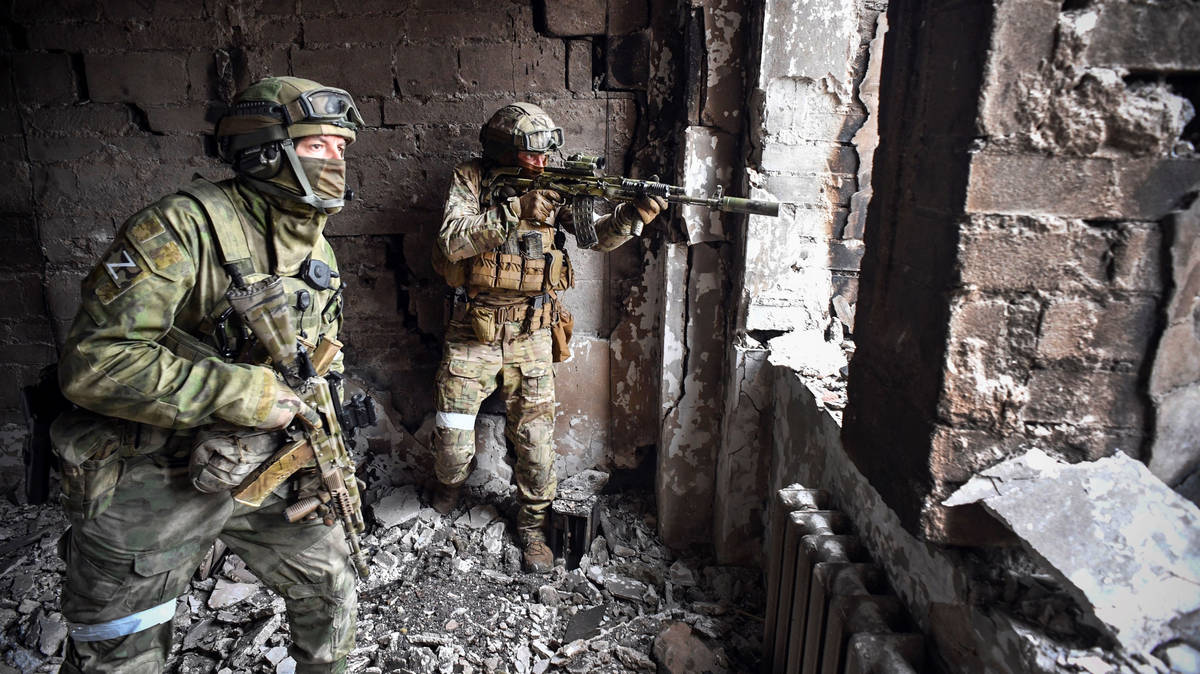
US intelligence reports indicate that Russian President Vladimir Putin may attempt to test NATO's resolve through small-scale provocations, including cyberattacks or limited land incursions, within the next few years. This marks a significant shift from previous assessments that deemed such actions unlikely while Russia is engaged in the Ukraine conflict. Intelligence suggests that these provocations could occur between autumn 2026 and 2029, with Poland identified as a potential target for drone or missile strikes. Recent incidents, including a Russian missile landing in Poland and drone incursions into Romania, have heightened concerns. Analysts warn that Putin's goal may be to fracture NATO unity and pressure Western allies to reduce military support for Ukraine. The situation remains fluid, with ongoing military actions from both Ukraine and Russia. The US has been providing intelligence and warnings to Eastern European allies about potential Russian plans.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (33)
Following this threat?
Track Wildberries in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…