 En.Vijesti.Me
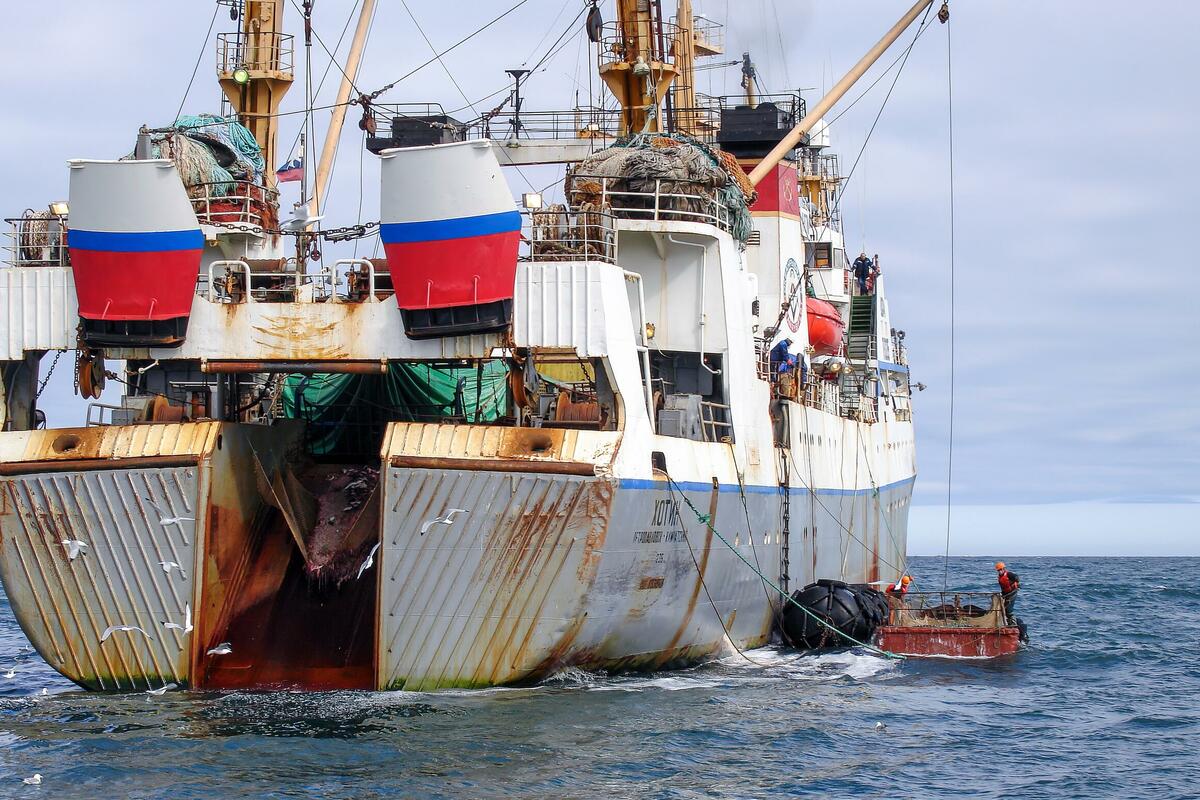
Russia Deploys Fishing Trawlers to Spy on UK Undersea Cables
Article Content

- •Over 500 incidents of Russian trawlers loitering above UK undersea cables have been reported.
- •NATO is tracking these vessels, which are suspected of espionage on behalf of Russia.
- •The UK government plans to implement stricter penalties for interference with undersea cables.
Russia is reportedly using fishing trawlers to spy on the UK's critical undersea cables, according to a recent analysis by The Telegraph. Over 500 incidents have been documented where these vessels loitered above or followed the routes of vital communications cables linking the UK with Europe and the US. This activity raises concerns about potential sabotage in future conflicts, as knowledge of the cables' precise locations could lead to significant disruptions in banking, healthcare, and telecommunications. NATO is monitoring these civilian ships, which appear to be operating without interference from the Royal Navy. The UK government is preparing to introduce tougher penalties for those who damage undersea cables, including lengthy prison sentences and unlimited fines. The Ministry of Defence has acknowledged the threat posed by Russian activities in UK waters and is increasing funding for the protection of critical infrastructure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Common questions
What specific actions is the UK government taking?
How many Russian trawlers are involved?
What are the potential impacts of these espionage activities?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…