 United24Media
Suspected Pneumonic Plague Case in Russia Triggers Quarantine Measures
Article Content

- •Darya Shipilova died from suspected pneumonic plague after a lab accident.
- •Around 200 individuals are under medical observation due to potential exposure.
- •U.S. and EU officials are monitoring the situation closely, seeking transparency from Russia.
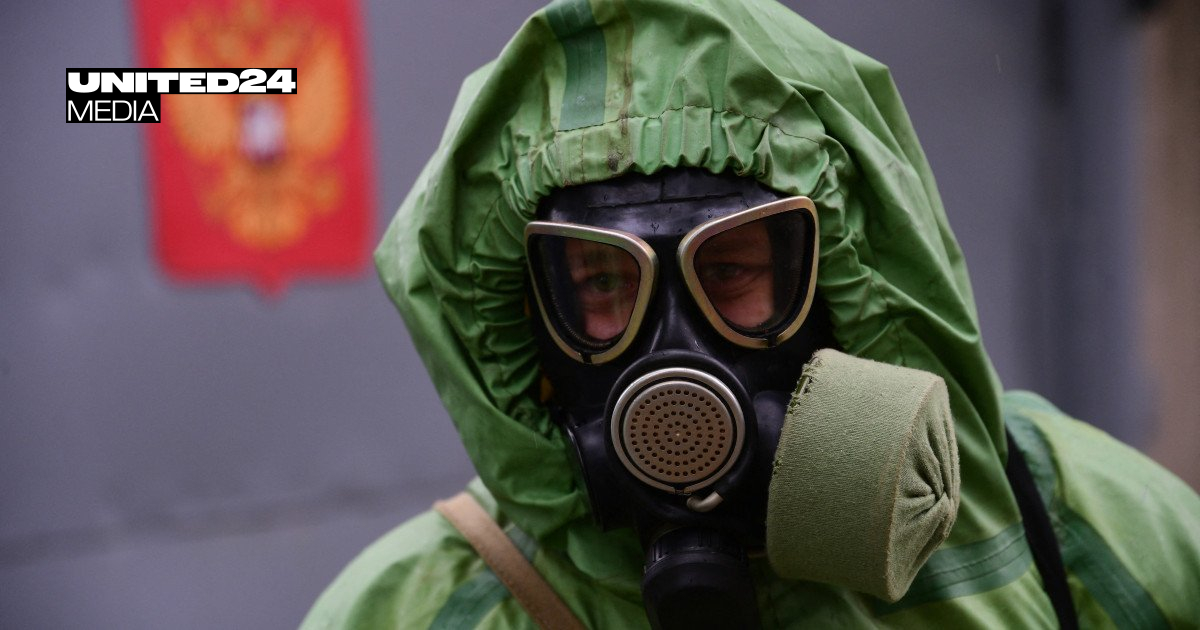
A 28-year-old lab technician, Darya Shipilova, died in Russia's Irkutsk region, with reports suggesting pneumonic plague as the cause. Following her death, nearly 200 individuals who had contact with her were placed under medical observation. Shipilova reportedly broke a test tube containing the plague pathogen while working at the Irkutsk Anti-Plague Institute. Russian health authorities have not confirmed the diagnosis, referring to her condition as 'pneumonia of unknown etiology.' Quarantine measures have been implemented in several hospitals, and mask mandates were introduced in local facilities. The U.S. and EU are closely monitoring the situation, urging Russian authorities for timely information. The incident has raised concerns over potential cover-ups by Russian officials regarding the outbreak.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (101)
Following this threat?
Track Irkutsk Anti-Plague Research Institute in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is pneumonic plague?
How many people are under observation?
What actions are authorities taking?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…