 Theguardian
Russia Launches Missile Attacks on Kyiv Amid Peace Talks
Article Content

- •Russia launched missile strikes on Kyiv, causing casualties and infrastructure damage.
- •The attacks occurred shortly after Putin agreed to resume peace negotiations with Ukraine.
- •Zelenskyy emphasized the need for stronger air defenses and sanctions against Russia.
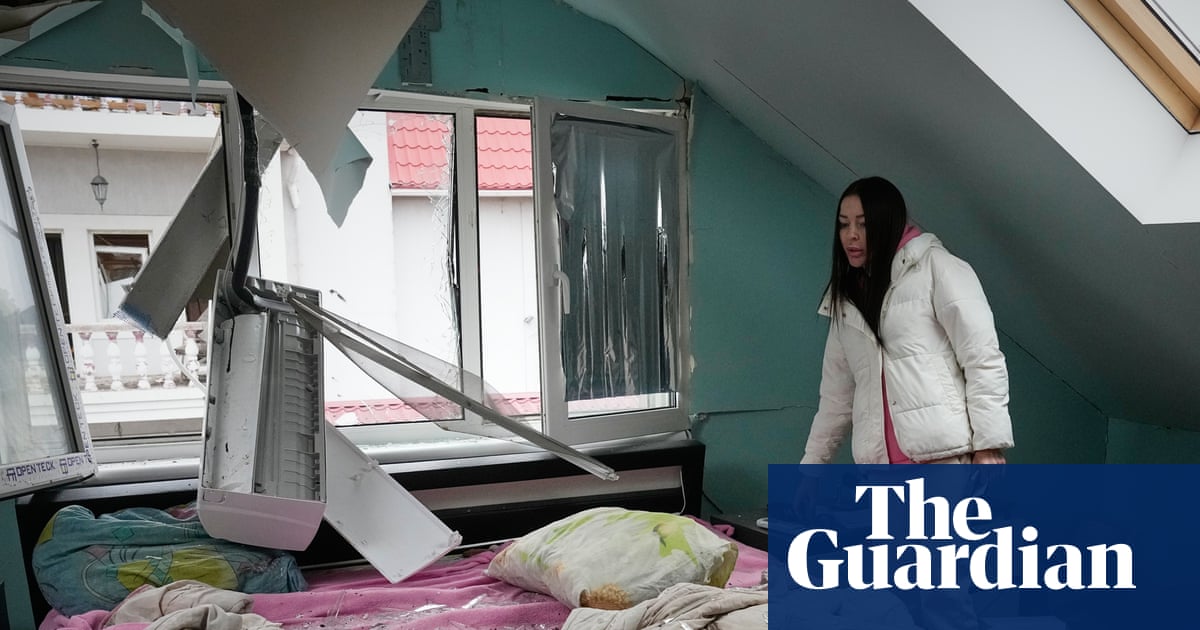
On October 22, 2026, Russia conducted a missile attack on Kyiv, killing at least two and injuring 22, including four children. This assault occurred just hours after Russian President Vladimir Putin agreed to resume trilateral negotiations with Ukraine, the US, and Russia. The strikes targeted various locations in Kyiv, including civilian infrastructure and energy facilities, raising concerns about Russia's intentions regarding peace talks. Ukrainian President Volodymyr Zelenskyy condemned the attacks, stating they demonstrated Russia's lack of seriousness about peace. The assault also affected other regions, including Odesa, where significant damage was reported. The Ukrainian government believes Russia aims to cripple Ukraine's energy infrastructure before winter. Zelenskyy called for enhanced air defenses and more sanctions against Moscow. The situation reflects ongoing tensions and the complexities of the conflict, as public sentiment in Ukraine shows a desire for negotiations, albeit without capitulation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track VKontakte in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What areas were affected by the missile strikes?
What was the response from Ukraine's leadership?
Are there ongoing negotiations between Ukraine and Russia?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…