 kyivindependent.com
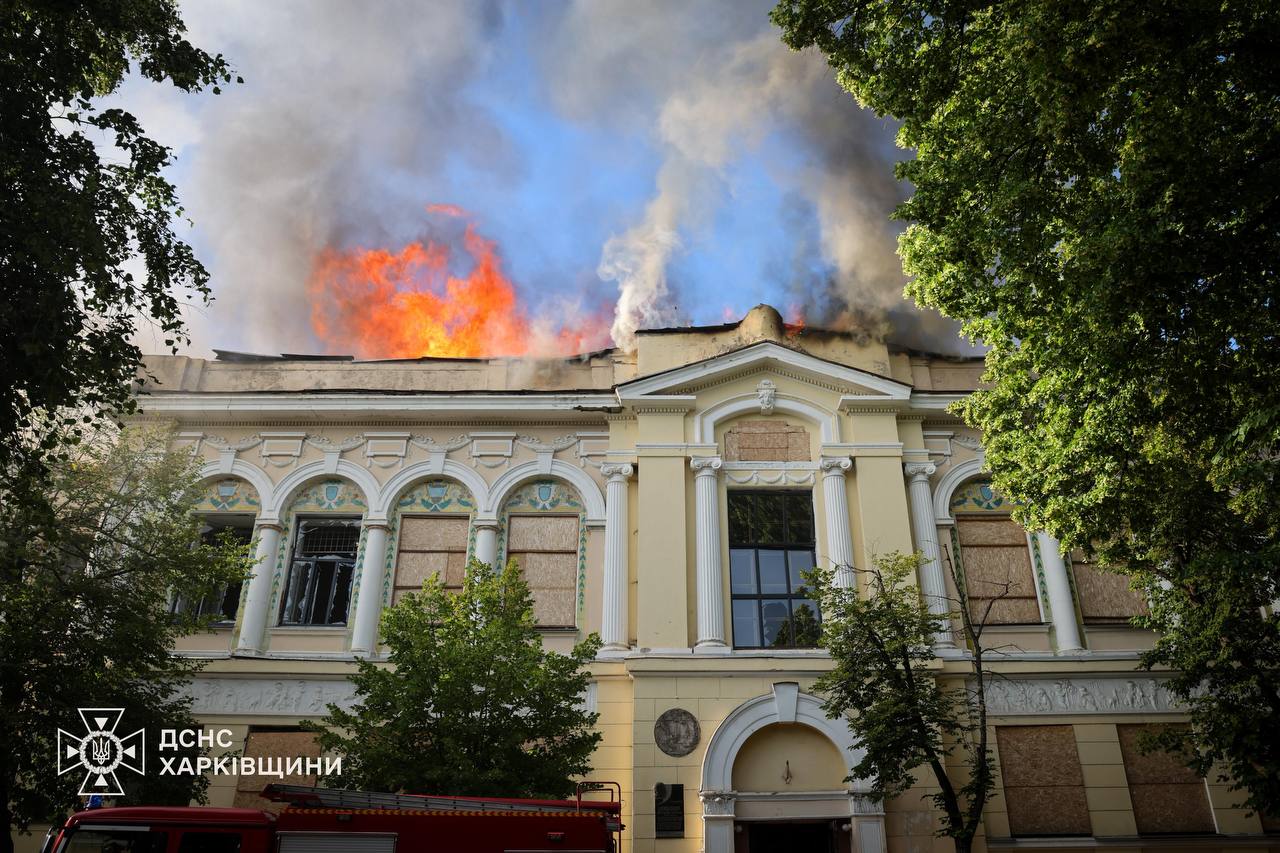
Russian Drone Strikes Target Kharkiv Art Museum, Cultural Heritage at Risk
Article Content

- •A Russian drone strike on June 14, 2026, severely damaged the Kharkiv Art Museum.
- •The attack injured five people, including a one-month-old infant, highlighting the risks to civilians.
- •This incident is part of a larger campaign targeting Ukraine's cultural heritage, with thousands of sites affected.
On June 14, 2026, a Russian drone strike hit the Kharkiv Art Museum, causing a major fire and injuring five individuals, including a one-month-old infant. The museum, housing a collection of 25,000 artworks, suffered extensive damage as locals rushed to evacuate valuable pieces. Regional Governor Oleh Syniehubov condemned the attack as an act of terrorism aimed at Ukraine's cultural heritage. This incident is part of a broader pattern of Russian attacks on cultural sites in Ukraine, with significant losses reported across various institutions. The ongoing strikes have led to the destruction of numerous cultural monuments, with estimates of damage to over 5,500 sites since the invasion began in 2022. Emergency response efforts are ongoing, and the situation remains critical as further attacks are anticipated.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Kharkiv Art Museum in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was damaged in the attack?
How many people were injured?
What is the current status of the museum?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…