 United24Media
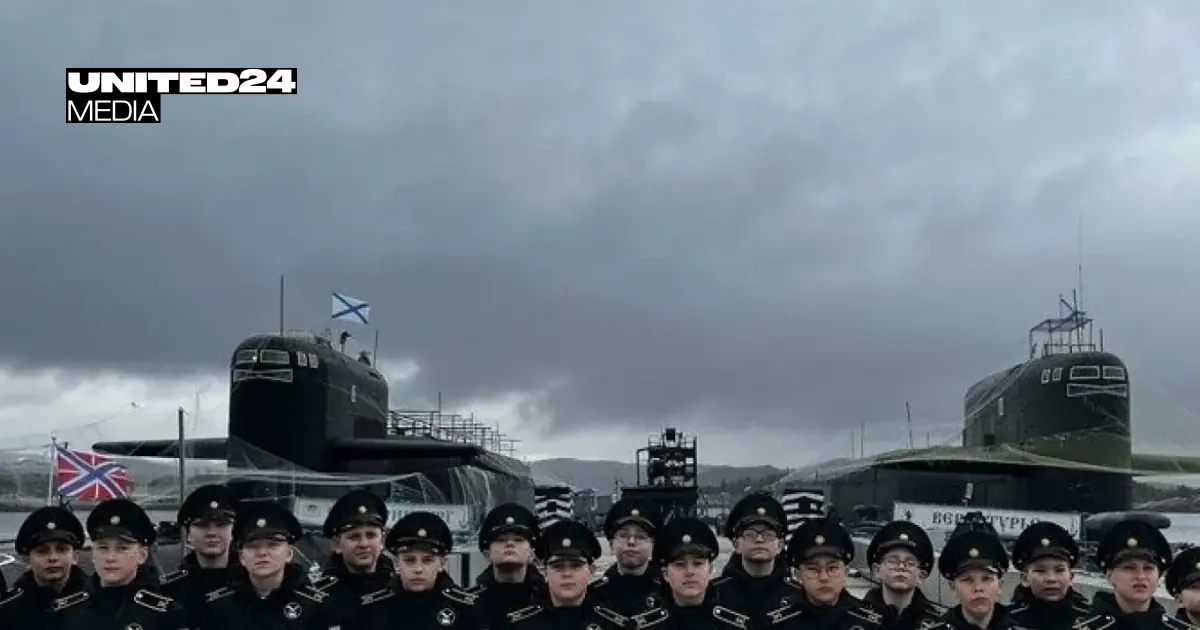
Russian Northern Fleet Enhances Submarine Security with Anti-Drone Nets
Article Content

- •Anti-drone nets have been deployed over Russian submarines at Gadzhievo naval base.
- •The measure is a response to concerns over Ukrainian drone attacks on military assets.
- •The netting is likely intended to protect against smaller quadcopter drones.
The Russian Northern Fleet has deployed anti-drone netting over its nuclear submarines at the Gadzhievo naval base, a first for this Arctic location. This installation follows increasing concerns about potential Ukrainian drone attacks targeting critical military assets. The netting covers key areas of the submarines, including torpedo tubes and missile compartments, although it remains unclear if the stern sections are similarly protected. Ukrainian forces have successfully conducted drone strikes against Russian military infrastructure, prompting this defensive measure. Experts suggest the nets are primarily designed to counter smaller quadcopter drones rather than larger drones capable of carrying heavier explosives. The move reflects a broader precautionary strategy rather than an immediate response to a specific threat. Similar netting has been reported at other Russian naval bases, indicating a trend in enhancing maritime security.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…