 Theguardian
Russia's Bauman University: Training Ground for GRU Hackers and Spies
Article Content

- •Bauman University secretly trains students for roles in Russian military intelligence.
- •Over 2,000 internal documents reveal the curriculum includes hacking and disinformation tactics.
- •Graduates are directly recruited into notorious hacking groups like Fancy Bear.
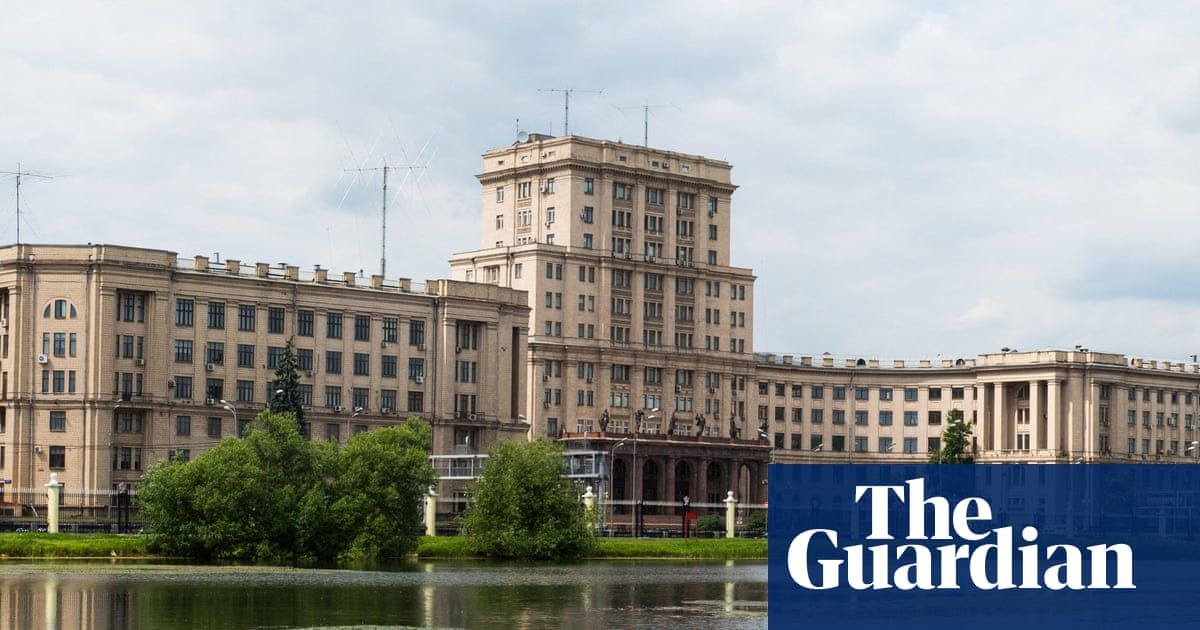
Bauman Moscow State Technical University is revealed to host a secret department training students for the GRU, Russia's military intelligence. Leaked documents show that over 2,000 students have been trained in hacking, cyber warfare, and disinformation tactics. Graduates, including Daniil Porshin, have joined notorious hacking units like Fancy Bear, implicated in various cyberattacks against Western targets. The university's Department No. 4 specializes in preparing operatives for roles in military intelligence, with direct oversight from the GRU. This program has been in operation for several years, with evidence of students being scouted directly from high schools. The revelations come amid ongoing accusations of Russian cyberattacks against EU institutions. The situation highlights a concerning trend of state-sponsored cyber operations emanating from Russia.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (15)
Following this threat?
Track notpetya, Fancy Bear and Bauman Moscow State Technical University in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploit in BeyondTrust Remote Support Disclosed BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE. The flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring credentials or user…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…