 Ua.News
Russia's Disinformation Campaign Targets Poland and Czech Republic Relations
Article Content

- •Russia is suspected of conducting a disinformation campaign to incite conflict between Poland and the Czech Republic.
- •Fake websites and social media accounts were used to spread false claims about territorial demands.
- •Polish officials have publicly condemned the disinformation and emphasized the importance of unity.
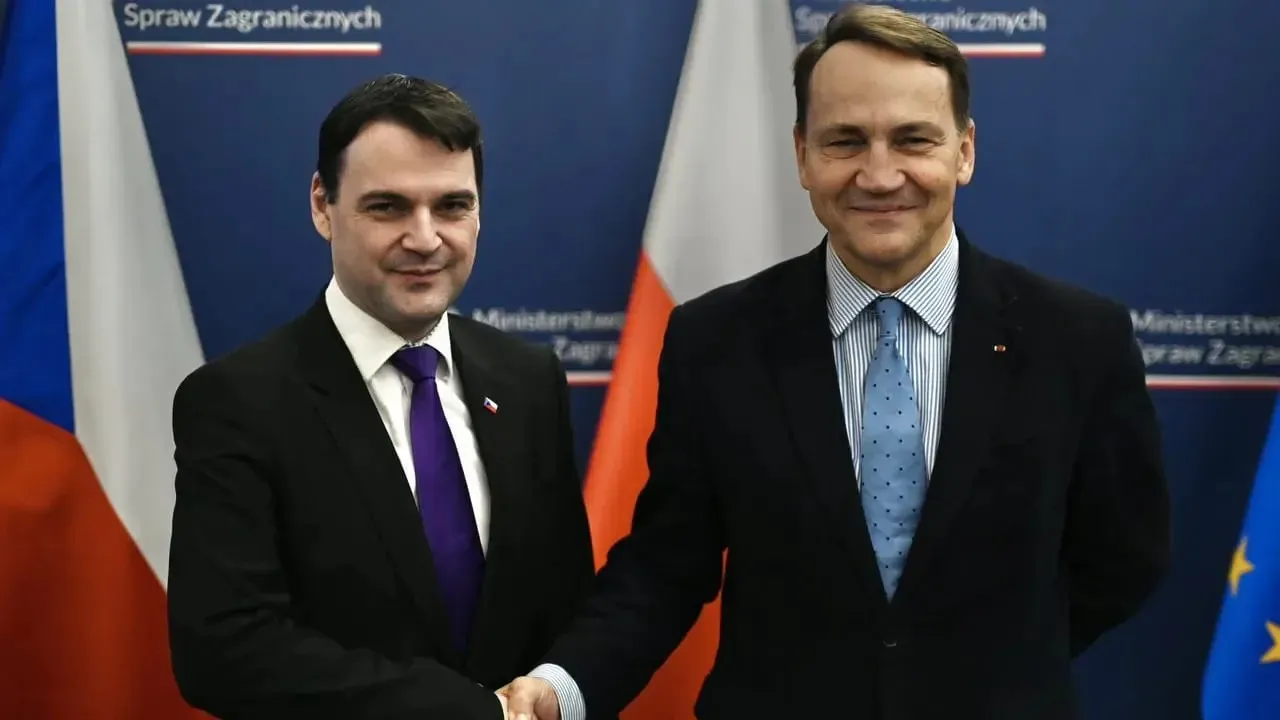
A disinformation campaign has been uncovered, allegedly orchestrated by Russia, aimed at creating discord between Poland and the Czech Republic. The campaign involved the creation of a fake 'Czech Radio' website and forged social media accounts to spread false claims about Poland's supposed territorial demands over 638 hectares of Czech land. The attackers circulated fake articles in Polish media and hacked the regional radio station Radio PiK to disseminate misleading information. Polish Foreign Minister Radosław Sikorski and Prime Minister Donald Tusk have publicly condemned the disinformation, urging unity between the two nations. The Czech Ministry of Foreign Affairs clarified that while there is a historical dispute over 368 hectares of land, the current claims are fabricated. The incident highlights the ongoing threat of state-sponsored disinformation campaigns in Europe.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Radio PiK in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…