 www.fdd.org
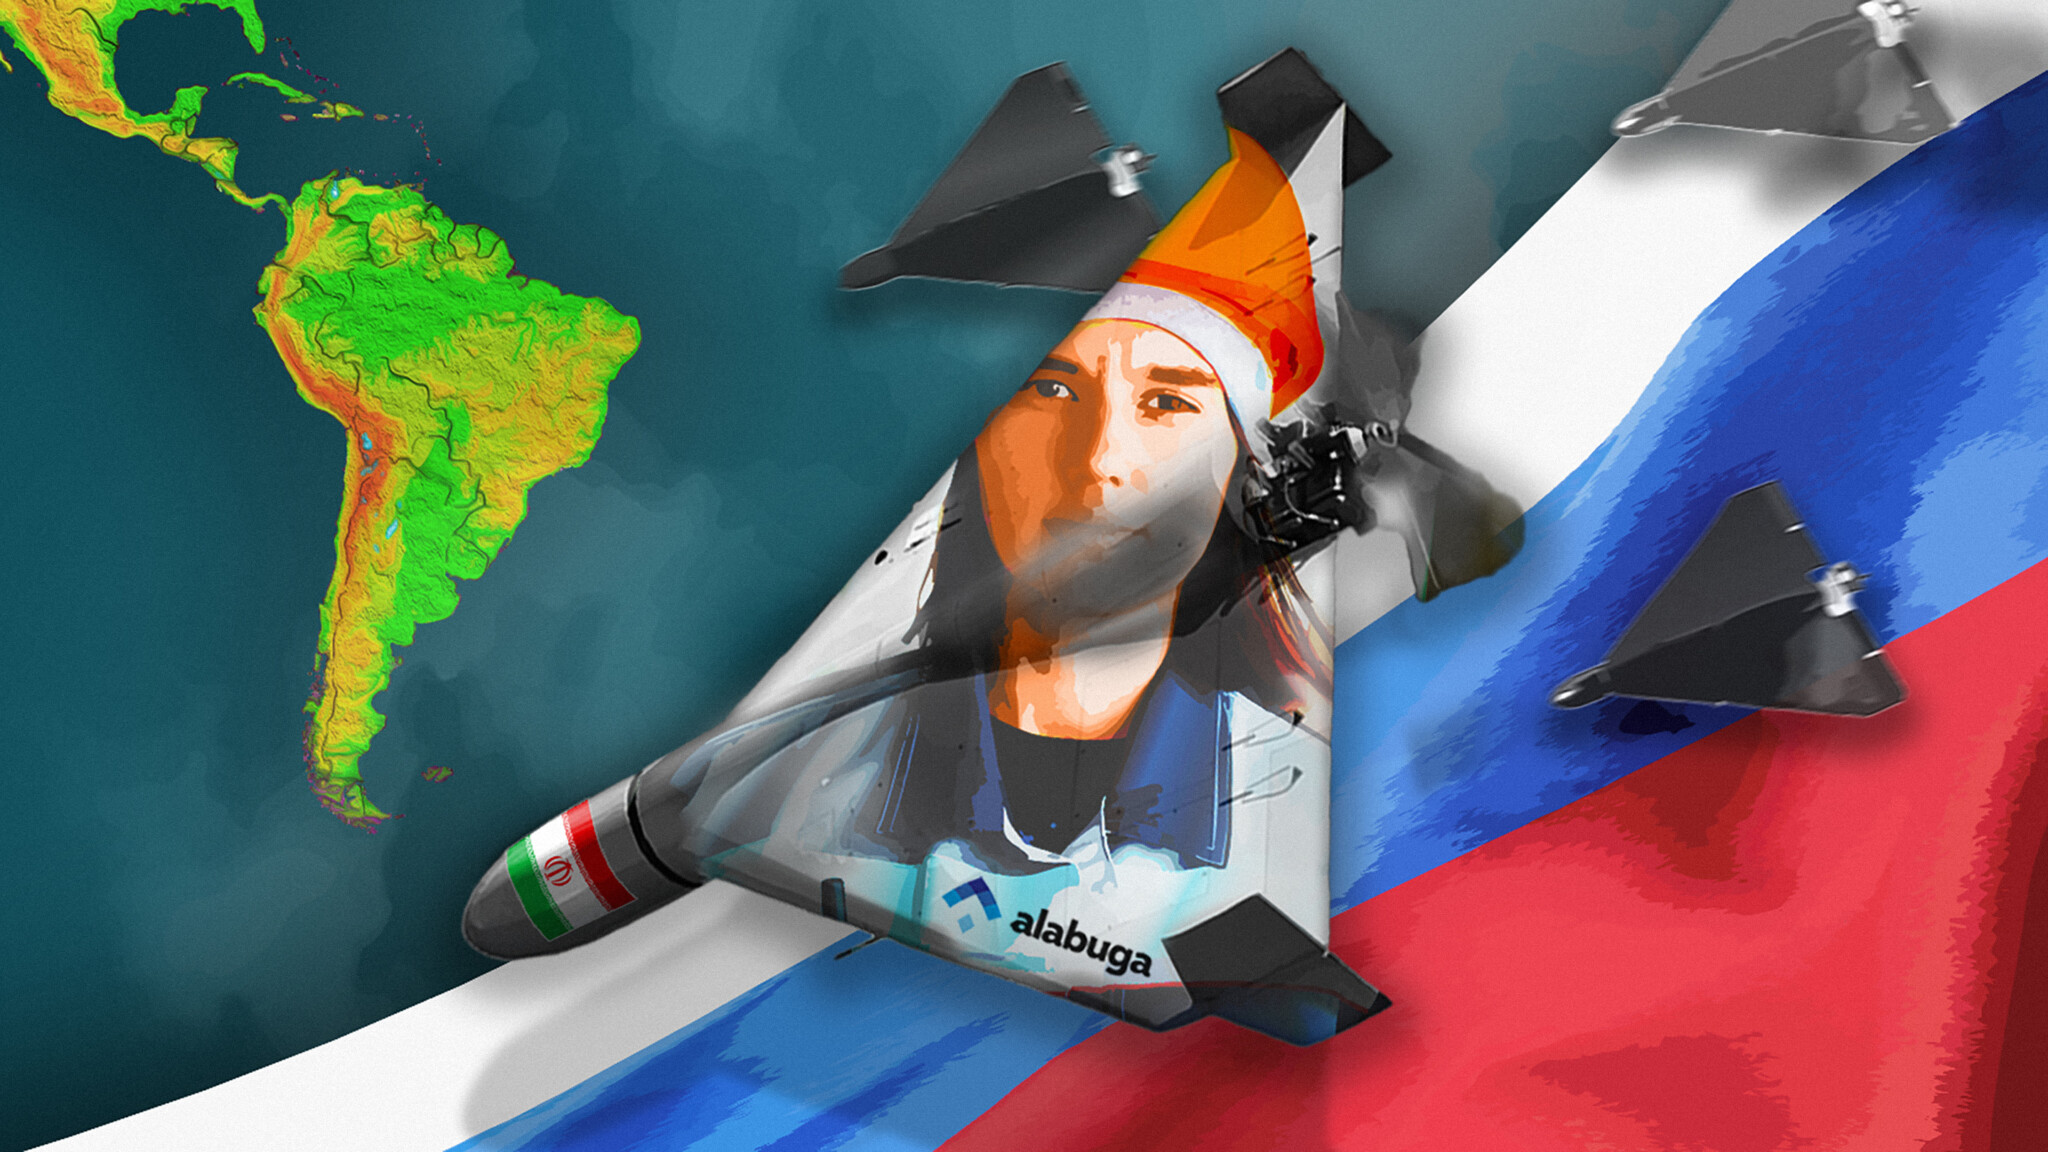
Russia's Recruitment of Latin American Women for Drone Production
Article Content

- •Russia is recruiting young women from Latin America for drone assembly under false pretenses.
- •The Alabuga Special Economic Zone is a key site for producing drones used in Ukraine.
- •The U.S. has sanctioned the Alabuga SEZ, but Russia's recruitment efforts continue to grow.
Russia is actively recruiting young women from Latin America under false pretenses to work in its drone production facilities, particularly in the Alabuga Special Economic Zone. This recruitment drive, part of a broader strategy to bolster drone manufacturing for its military operations in Ukraine, has expanded from Africa to at least 12 Latin American countries. The program, named Alabuga Start, falsely advertises high wages and educational opportunities, but recruits face harsh working conditions. Concurrently, Russia's Alabuga Polytech is also recruiting young men to form a new unmanned systems brigade, offering financial incentives to avoid conscription. The Geran-2 drones produced at these facilities are used in attacks against Ukrainian infrastructure. The U.S. has imposed sanctions on the Alabuga SEZ and its affiliates, but Russia continues to expand its labor pipeline. The situation raises serious human rights concerns and highlights the intersection of labor exploitation and military aggression.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Alabuga Polytech in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…