 Kyivindependent
Russia's Shadow Fleet Utilizes Starlink for Sanctions-Evasion Operations
Article Content

- •Russia's shadow fleet uses Starlink for communication, facilitating sanctions evasion.
- •Approximately 3,240 vessels are involved in transporting sanctioned oil globally.
- •Ukrainian officials demand action from SpaceX to prevent misuse of Starlink technology.
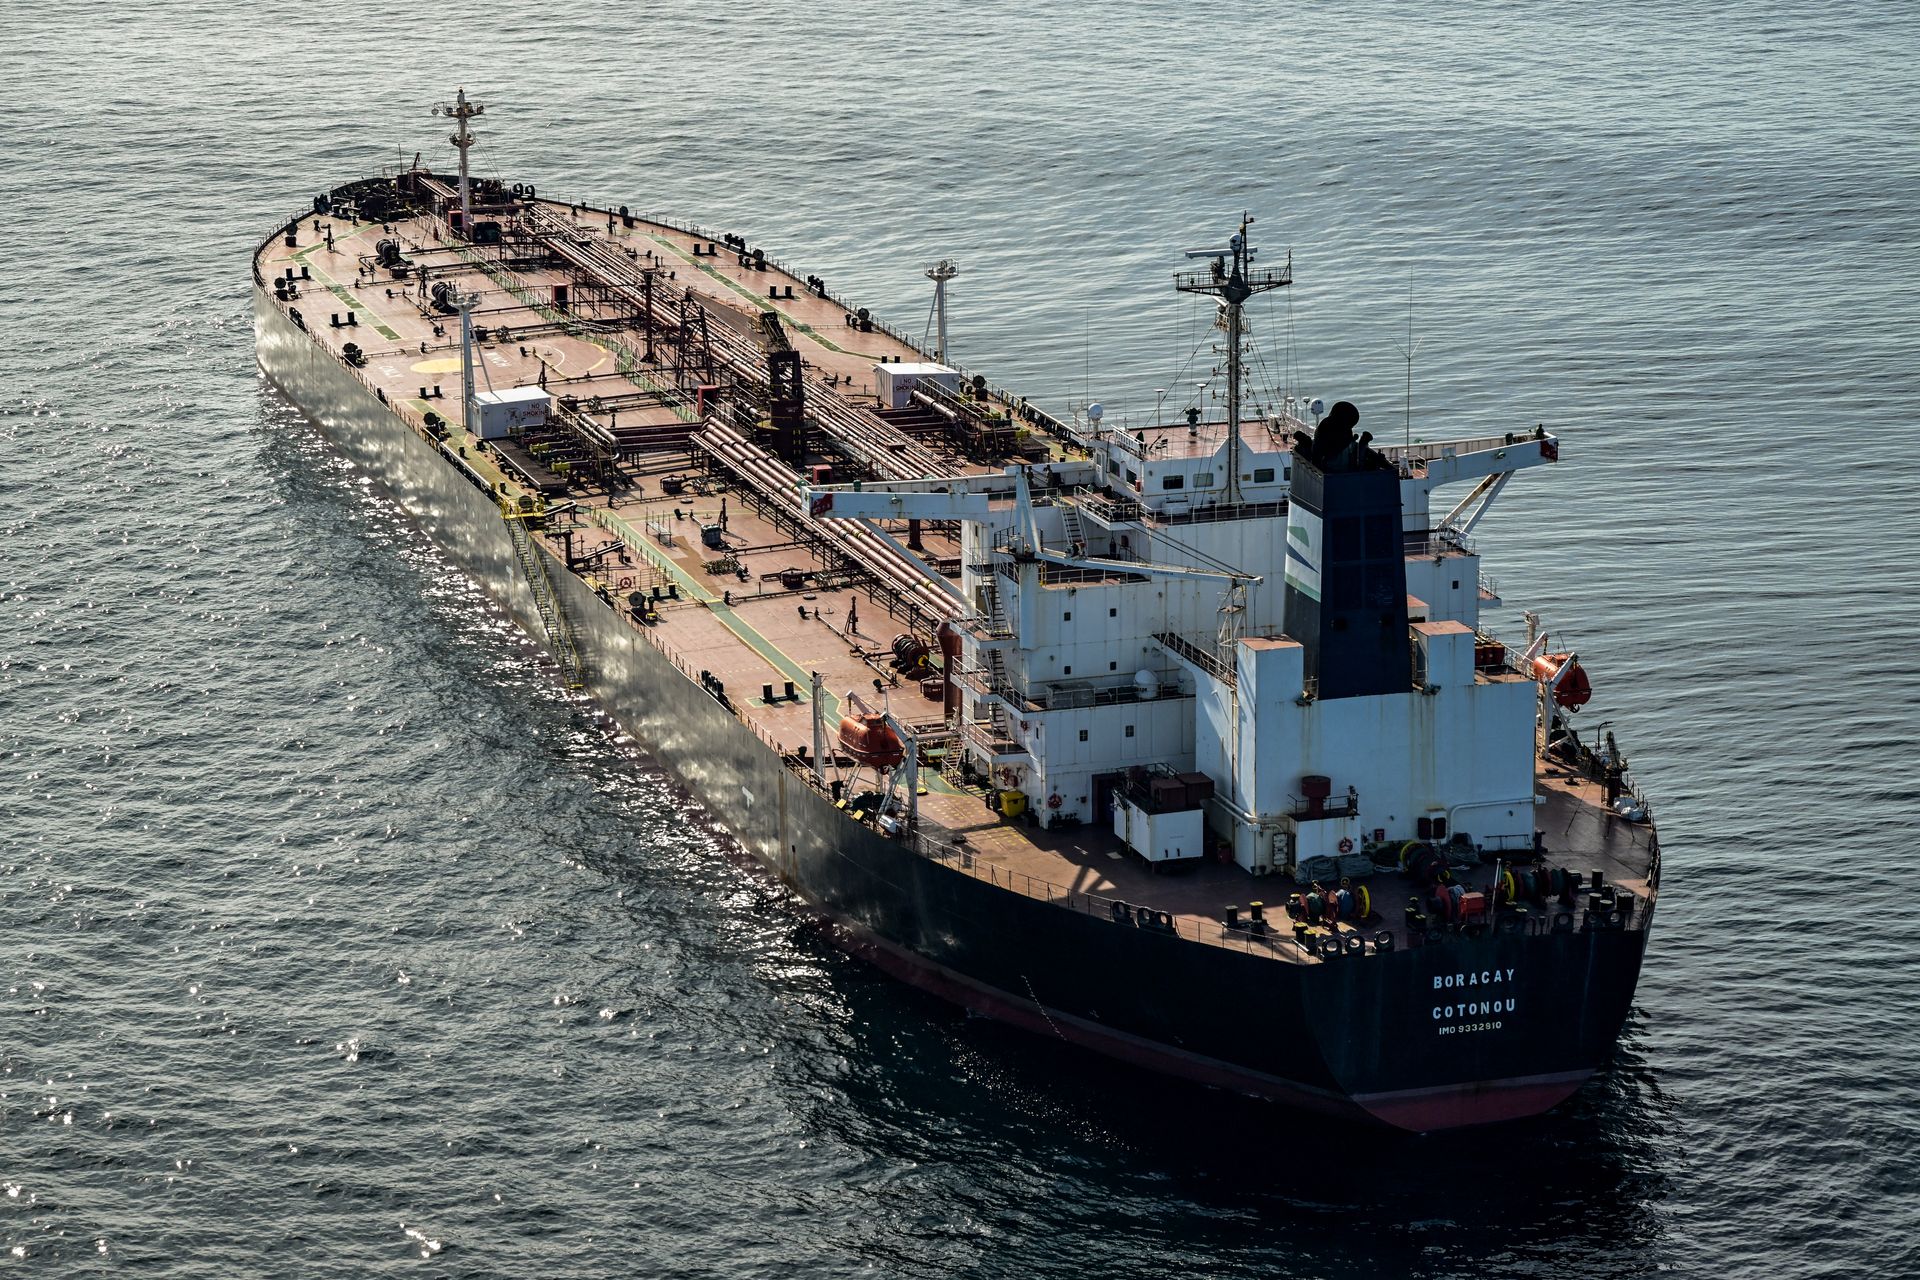
An investigation by the Kyiv Independent reveals that Russia's shadow fleet, responsible for moving sanctioned oil globally, employs Starlink technology for communication and coordination. Ukrainian sailors, recruited under false pretenses, reported that they unknowingly participated in this operation, which funds Russia's invasion of Ukraine. The fleet consists of approximately 3,240 vessels, with 600 sanctioned by the EU and 500 by the UK. The use of Western technology, including Starlink, raises concerns about complicity in evading sanctions. Ukrainian officials have called on SpaceX to take action against the misuse of its technology. The investigation highlights the sophisticated methods used by Russia to obscure vessel ownership and operational details. The ongoing conflict and sanctions against Russia complicate maritime safety and international shipping regulations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…