 Philstar
School Shooter Linked to Deep Dark Web Influence
Article Content

- •The shooter was heavily influenced by content from the deep dark web.
- •The attack resulted in two fatalities and eight injuries, with two in critical condition.
- •Authorities are considering new laws to restrict minors' access to harmful online content.
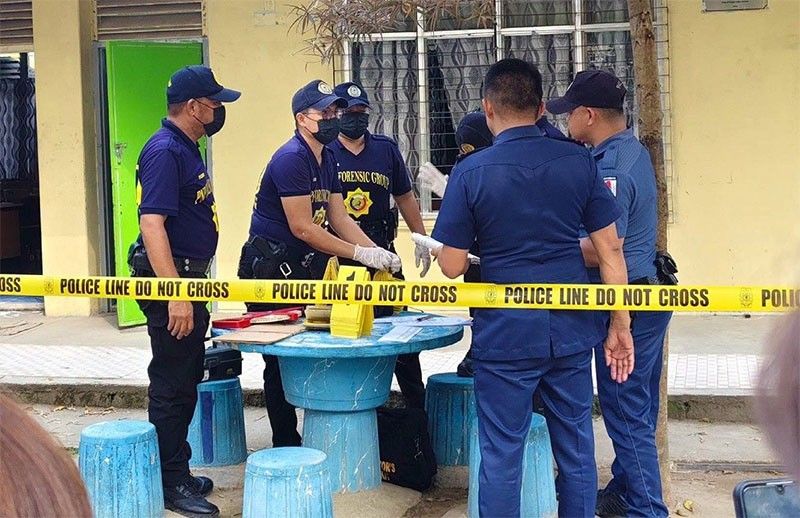
A 16-year-old student at Banga National High School in South Cotabato went on a shooting spree, killing two classmates and injuring eight others before taking his own life. The shooter was reportedly suffering from depression and had accessed harmful content on the deep dark web, which authorities believe influenced his actions. The firearm used in the attack belonged to his father, a disaster risk mitigation officer for the Department of Education, and was not properly secured. The incident has raised concerns about the accessibility of violent content online, prompting calls for legislative action to limit minors' access to social media platforms. The shooter had left notes detailing his mental struggles, which his parents discovered earlier this year. This incident is part of a troubling trend of school shootings in the Philippines, following similar attacks in Tacloban and Zamboanga City earlier in 2026.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Education in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…