 Shattered
Self-Driving Vehicle Software Complexity Demands Deeper Cybersecurity Analysis
Article Content

- •The argument is advisory: autonomous driving stacks are described as more complex than traditional ECU threat models assume, with no specific exploited flaw reported.
- •Recommended assessment scope includes source code review, runtime behavior analysis, and safety-critical data flows.
- •Middleware, shared memory, message queues, and software dependencies are named as expanding the attack surface.
- •Localization, planning, and vehicle control are identified as priority areas where tampered data could change vehicle behavior.
- •Cited standards are ISO/SAE 21434 and UNECE R155; no CVEs or IOCs are provided in the coverage.
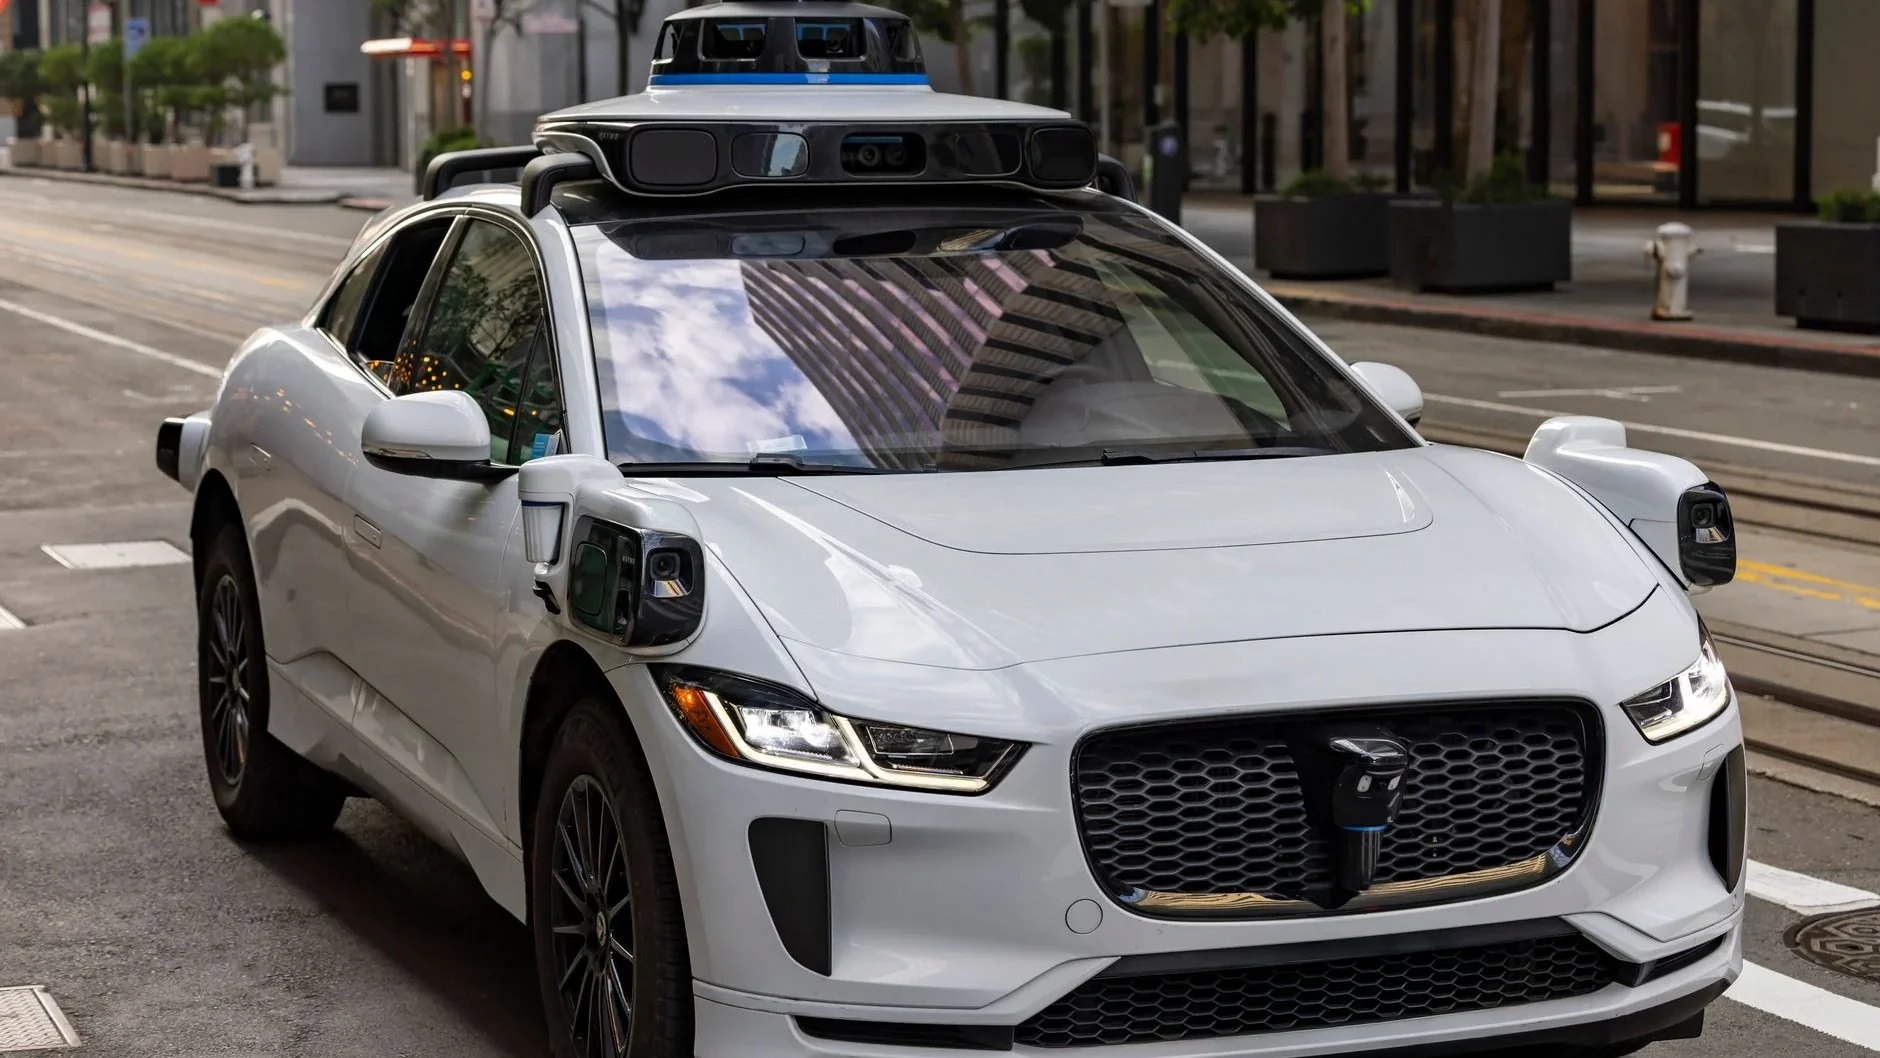
Mobility Engineering published an article titled 'Self-Driving Vehicles Demand New Cybersecurity Thinking,' listed October 1, 2026, arguing that autonomous driving stacks combining AI models, middleware, safety mechanisms and vehicle integration code create risks beyond traditional vehicle threat modeling. A PlusAI-authored piece on the Mobilityengineeringtech site makes a similar argument, stating that ISO/SAE 21434 and UNECE R155 provide a foundation but architecture-level analysis may not reveal the full attack surface. Both pieces recommend examining source code, runtime behavior and safety-critical data flows, and identify middleware, shared-memory regions, message queues and software dependencies as widening the attack surface. The reporting names localization, planning and vehicle control as priority areas, since tampered data there could alter on-road behavior. The Shattered article ties the argument to regulatory pressure on robotaxi operators, citing a report that Waymo has been barred from California freeways since November 11, though it states that case concerns safety rather than hacking. The available coverage describes no specific vulnerability, CVE, attack, or confirmed exploitation. Full text of the Mobility Engineering article was not available to the Shattered reporter, so its specific claims are not independently verified.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
Are there specific vulnerabilities in autonomous driving software reported here?
Which components should defenders prioritize for review?
Does this change current compliance requirements?
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…