 www.sevii.com
Sevii Launches AI-Driven Autonomous Defense Against Cyber Threats
Article Content

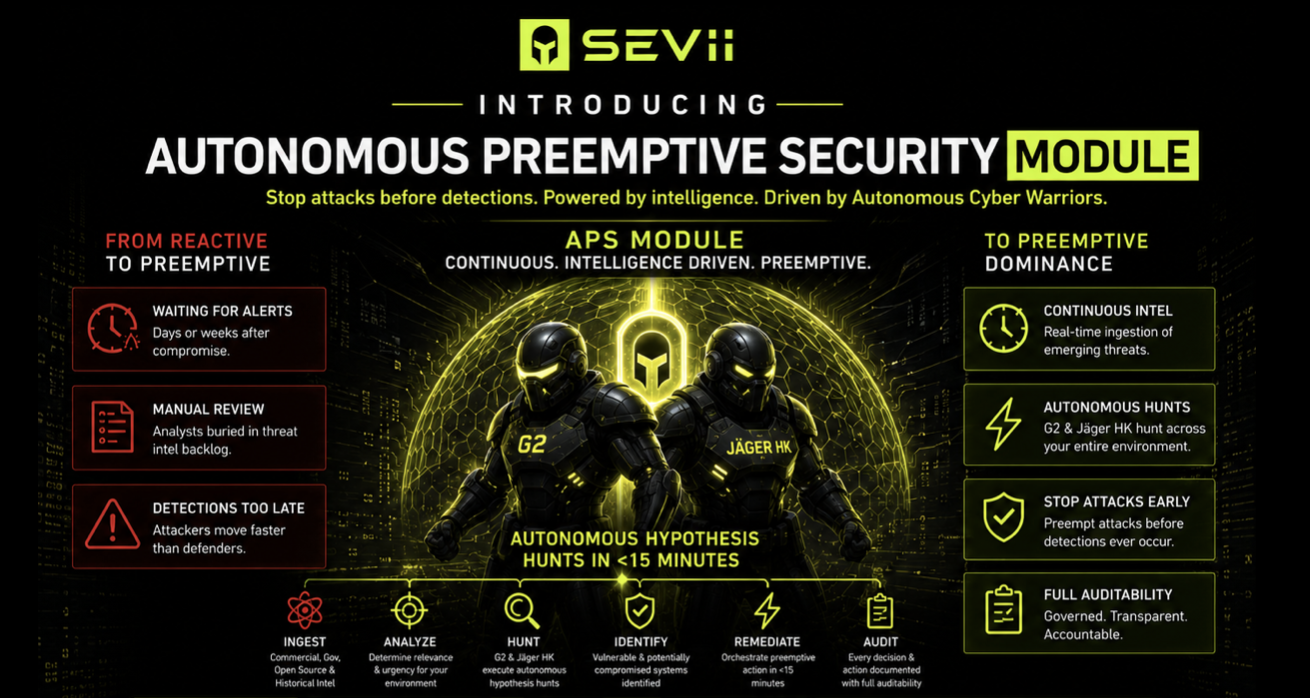
- •Sevii's new APS module enhances its ADR platform for proactive AI threat defense.
- •The module autonomously transforms cyber intelligence into immediate remediation actions.
- •AI-driven attacks require defenses that can operate at machine speed to be effective.
On September 1, 2026, Sevii announced the expansion of its Autonomous Defense & Remediation (ADR) platform with a new Autonomous Preemptive Security (APS) module. This module aims to counter AI-driven cyber threats by autonomously transforming real-time cyber intelligence into remediation actions. It addresses the challenge of 'Dark AI' adversaries who exploit vulnerabilities faster than human defenders can react. The APS module enhances Sevii's existing capabilities by enabling proactive hypothesis hunting and immediate remediation of potential threats. CEO Curt Aubley emphasized that the speed of AI attacks necessitates equally rapid defensive measures. The platform is designed to operate continuously, validating exposures and containing threats before they escalate. This innovation is particularly relevant in the evolving landscape of cyber warfare, where attackers leverage AI for rapid exploitation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Nutex Health in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…