 Securityweek
Siemens Software Center Vulnerability Exploited in ClickFix Malware Campaign
Article Content

- •CVE-2026-110936 is actively exploited, allowing DLL side-loading attacks.
- •Siemens has released an automatic patch for affected users.
- •The attacks are associated with the Romulus ClickFix malware campaign.
Siemens confirmed that a vulnerability in Siemens Software Center (CVE-2026-110936) is being in a malware campaign. The flaw allows authenticated local attackers to execute malicious DLL files due to improper DLL file location restrictions. Siemens released a patch (version 4.0.9.8) on October 15, 2026, which automatically updates existing installations. The attackers used a legitimate version of the software, which was not tampered with, to load their malicious files. Siemens has engaged with EDR vendors and authorities for threat intelligence sharing. The attacks are linked to the Romulus ClickFix operation, which employs fake prompts to trick users into executing malicious commands. Indicators of compromise (IoCs) have been shared to aid detection and response efforts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Chinese APT, ClickFix and Siemens in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which versions of Siemens Software Center are affected?
What should I do if I am using Siemens Software Center?
How are attackers exploiting this vulnerability?
Continue Reading
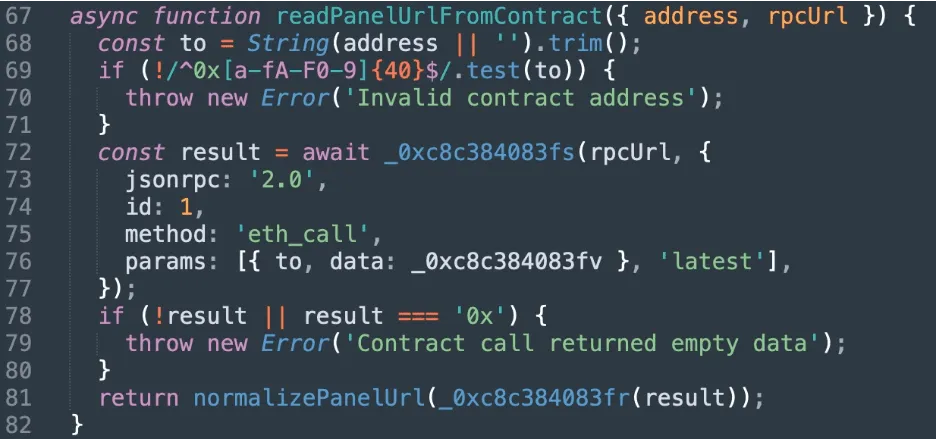 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…