 Itweb.Africa
Sierra Leone Launches Campaign Against AI Deepfakes
Article Content

- •Sierra Leone's campaign targets AI-generated deepfakes and misinformation.
- •The initiative includes public workshops and media outreach to raise awareness.
- •Verification tools will be introduced to help citizens identify manipulated content.
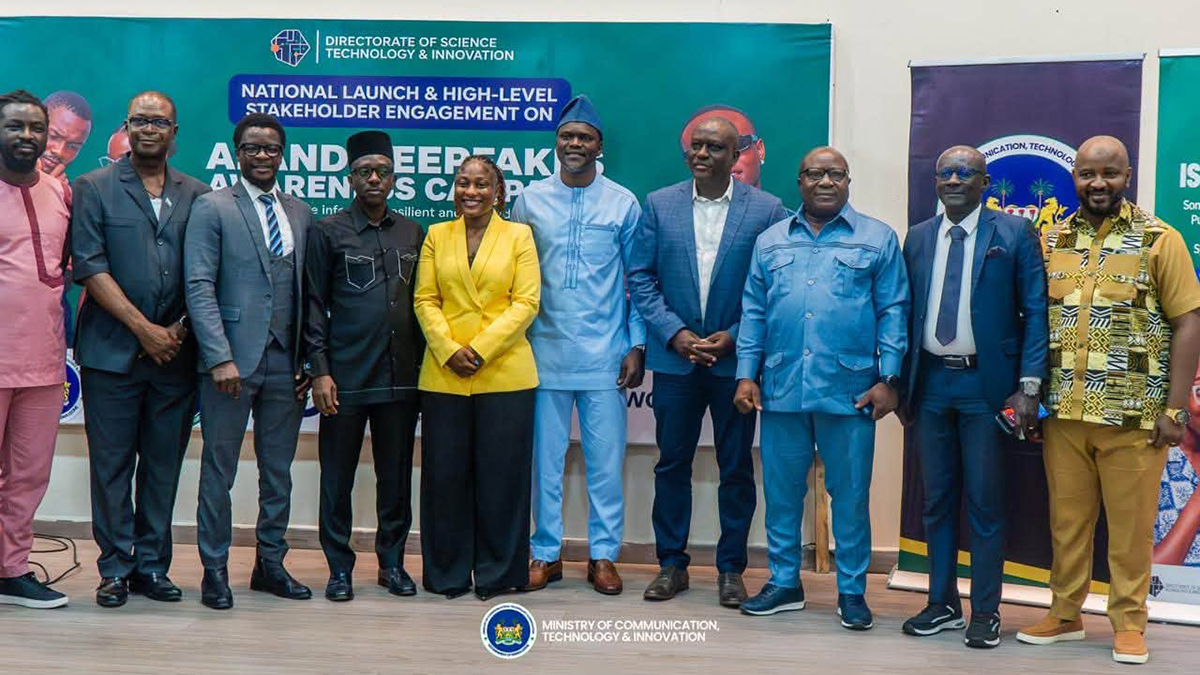
On September 17, 2026, Sierra Leone initiated the National AI and Deepfake Awareness Campaign to combat the risks posed by AI-generated deepfakes. The campaign, led by the Directorate of Science, Technology and Innovation, aims to educate citizens across all 16 districts about identifying manipulated content. The first phase focuses on public awareness through community workshops and media outreach, particularly targeting those with limited internet access. The second phase will introduce verification tools, including a WhatsApp service and a low-bandwidth app for reporting harmful content. Officials highlighted the dangers of AI-generated scams, such as fake voice messages requesting money. The initiative is supported by the World Bank through the Sierra Leone Digital Transformation Project. The government emphasizes the importance of protecting trust in information while ensuring freedom of expression. This campaign follows the enactment of the Cyber Security and Crime Act in 2021, as the country addresses the increasing risks associated with digital connectivity.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…