 Finance.Biggo
South Korea Launches Support Program for Voice Phishing Victims
Article Content

- •FSS's new program offers up to 2 million won for voice phishing victims.
- •Support includes emergency living expenses and mandatory psychological counseling.
- •Applications open on November 23, 2026, for eligible victims.
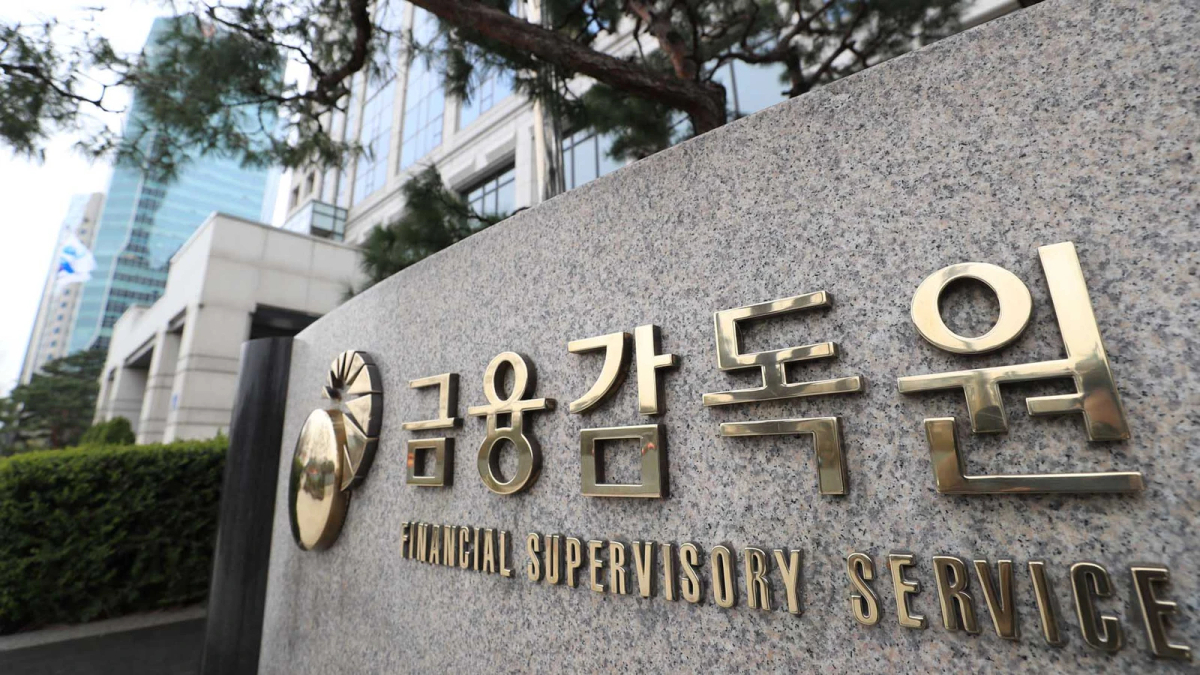
On November 9, 2026, South Korea's Financial Supervisory Service (FSS) announced a pilot program to aid voice phishing victims, providing up to 2 million won (approximately $1,500) in living expenses and psychological counseling. The initiative, named 'Back to Daily Life,' will support 200 victims who have suffered losses since 2024 and have a household income below 150% of the median. Eligible victims will receive an initial payment of up to 1 million won as emergency living expenses, followed by an additional 1 million won after completing six counseling sessions. The program aims to address both financial and psychological impacts, as many victims experience guilt and anxiety due to prolonged manipulation by scammers. Applications will be accepted starting November 23, 2026, and the program may end early if funds are exhausted. The FSS reported a significant decrease in voice phishing cases this year, but the psychological toll on victims remains a concern.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
Who is eligible for the support program?
What is the application process?
What kind of support will victims receive?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…