 Straitstimes
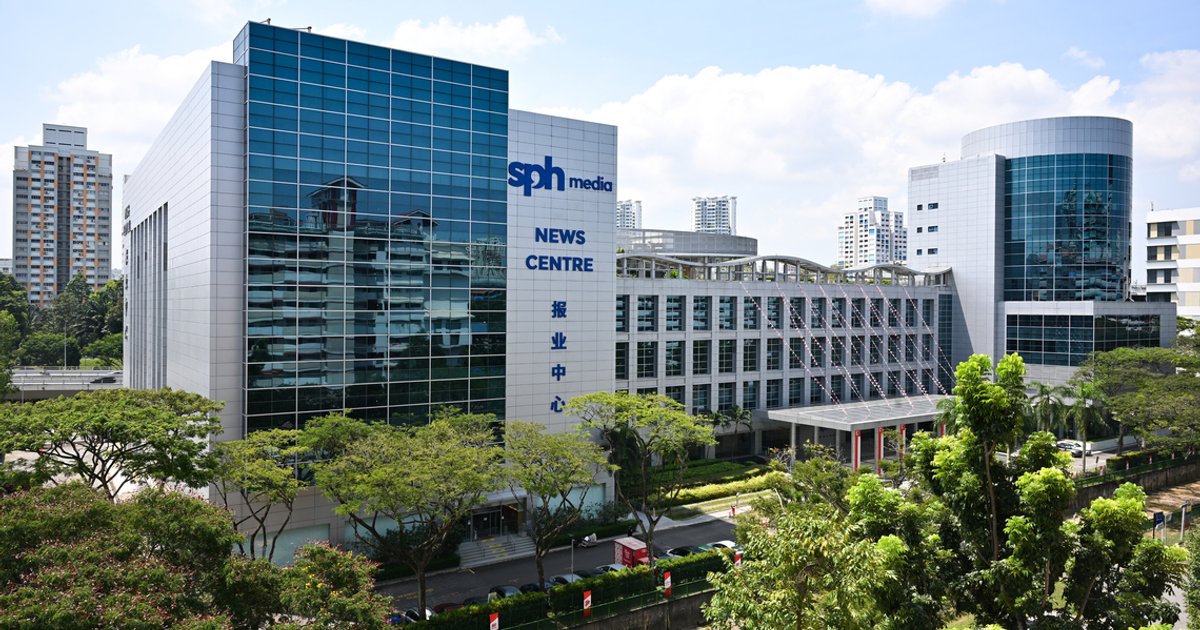
SPH Media Suffers AI-Enabled Cyberattacks, 9% of Database Affected
Article Content

- •SPH Media experienced cyberattacks affecting 9% of its database.
- •No financial data or payment information was compromised in the breach.
- •The attacks are suspected to be AI-enabled and executed by a single threat actor.
On November 10, 2026, SPH Media reported being targeted by cyberattacks that compromised 9% of its database, primarily exposing email addresses, names, mailing addresses, and phone numbers. The attacks, which occurred between November 4 and November 8, are suspected to be AI-enabled and orchestrated by a single threat actor. No financial information, payment card details, or customer account access were compromised. SPH Media identified vulnerabilities due to software bugs and system configuration issues. The company has engaged external cybersecurity experts to investigate and mitigate the breaches, and has reported the incidents to relevant authorities, including the Personal Data Protection Commission and the Cyber Security Agency of Singapore. Customers have been advised to remain vigilant against unsolicited communications. SPH Media has since implemented bug fixes and enhanced its cyber defenses to prevent future incidents.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Doctor Anywhere in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data was compromised?
How did the breach occur?
What should affected customers do?
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical RCE and LPE Vulnerabilities in Quest Foglight for Databases On November 3, 2026, the Zero Day Initiative disclosed multiple critical vulnerabilities in Quest Foglight for Databases, including six remote code execution (RCE) flaws and two local privilege escalation (LPE) vulnerabilities. The most severe RCE vulnerabilities, CVE-2026-92189 and CVE-2026-92190, allow…