 store.steampowered.com
Spymaster Launches with Unique Time-Rewind Feature for VR Espionage
Article Content

- •Spymaster launched on October 16, 2026, after five months in Early Access.
- •The game features a time-rewind mechanic via the C.A.S.S.E.T.T.E. device.
- •Players control three unique agents to complete various espionage missions.
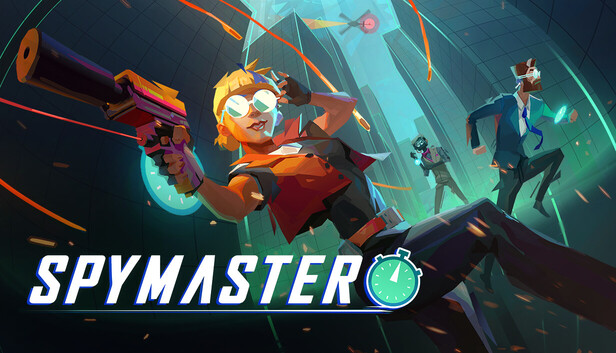
Spymaster, developed by InnerspaceVR, officially launched on October 16, 2026, after five months in Early Access. The game features a unique mechanic using the C.A.S.S.E.T.T.E. device, which allows players to rewind time during missions to correct mistakes and optimize strategies. Players control three distinct agents, each equipped with unique skills and weapons, to complete various espionage missions. The game is available on platforms including Quest and Steam, enhancing its accessibility for VR gamers. The full release includes four new missions that conclude the campaign, adding to the replayability and charm characteristic of Innerspace's previous titles. There are no reported cybersecurity threats or vulnerabilities associated with the game’s launch.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Quest in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What platforms is Spymaster available on?
What is the unique feature of Spymaster?
How many missions does Spymaster include?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…