 Enlit.World
SQC Secures AU$3.6M for Quantum AI Energy Forecasting Project
Article Content

- •SQC and Schneider Electric received AU$3.6 million for a quantum AI energy project.
- •The Watermelon chip aims to improve energy forecasting accuracy by 20% using quantum-enhanced AI.
- •The project will expand modeling to hundreds of homes, integrating with existing AI workflows.
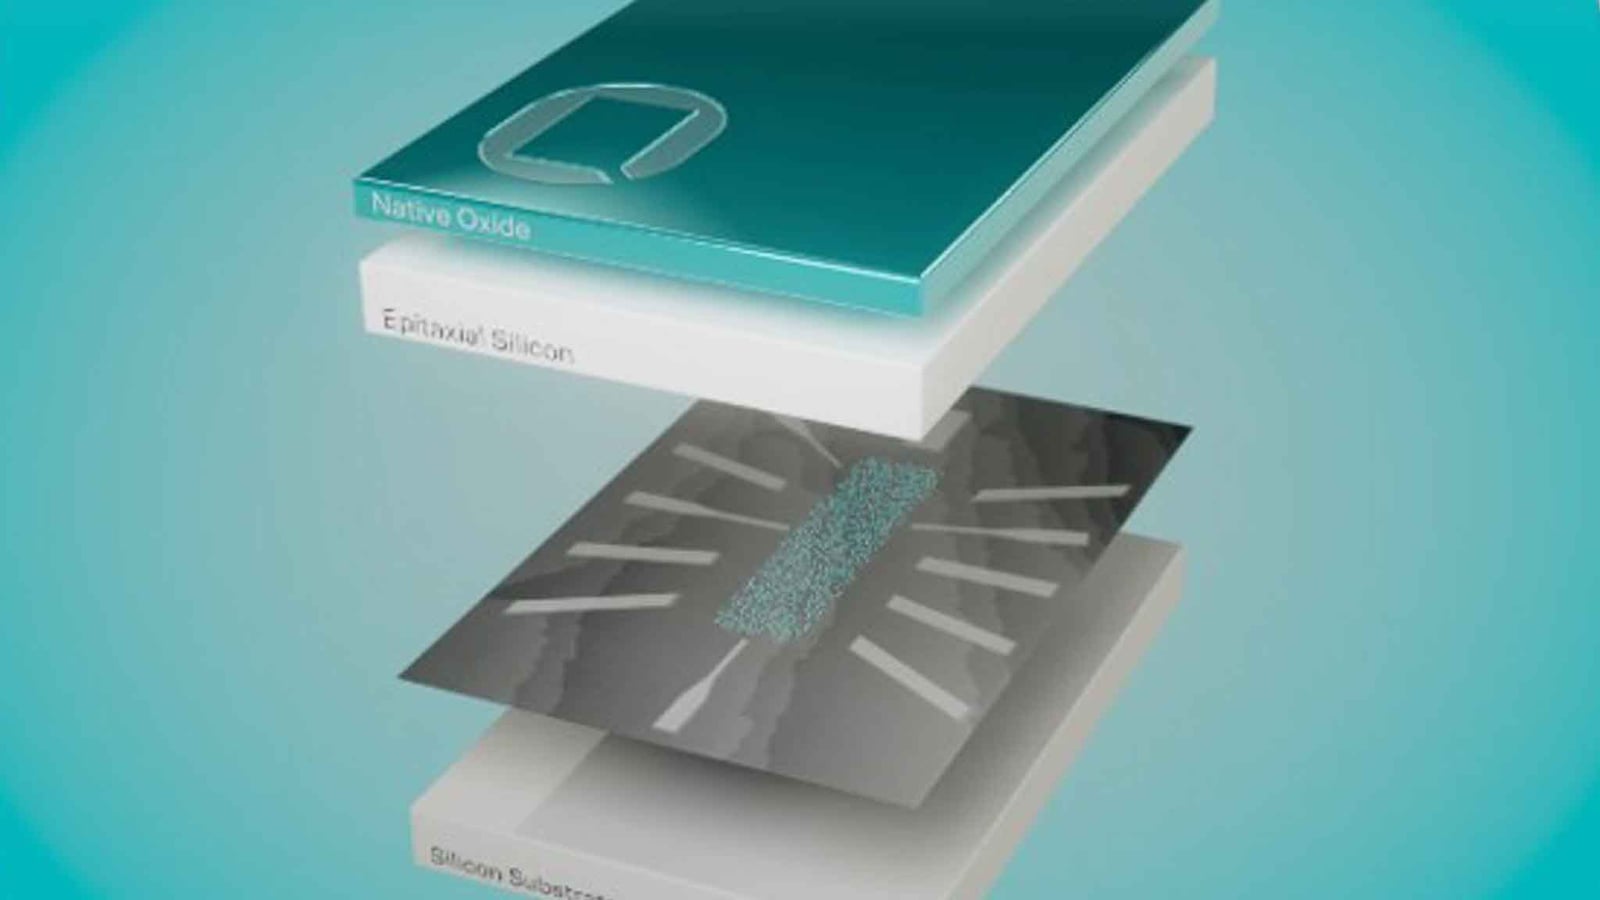
Silicon Quantum Computing (SQC) and Schneider Electric have received AU$3.6 million to enhance energy forecasting using a quantum-enhanced AI chip named Watermelon. This funding, part of the Critical Technologies Challenge Program, aims to improve forecasting accuracy by 20% for energy consumption in Australian households. The project will integrate quantum features with classical data to better manage the complexities of energy systems, particularly as renewable energy sources like solar power and electric vehicles become more prevalent. Initial tests showed a 20% improvement in forecasting accuracy, with potential gains reaching 41%. The funding will allow the expansion of modeling to hundreds of homes across Australia, directly integrating into Schneider Electric's AI workflows. The initiative is expected to contribute to lower energy costs for consumers and enhance grid resilience.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Schneider Electric in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the Watermelon chip?
How much funding did SQC receive?
What are the expected benefits of this project?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…