 Newswire.Lk
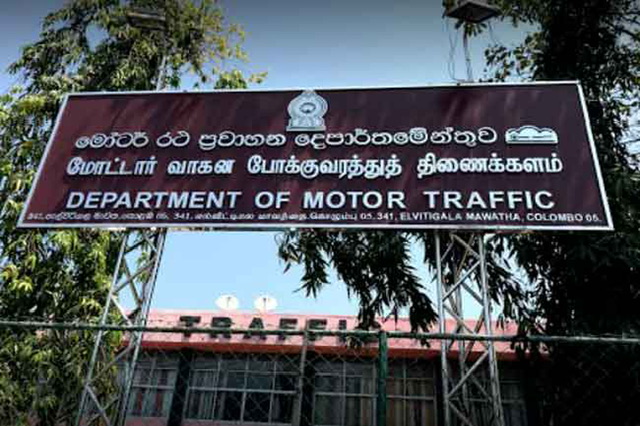
Sri Lanka Department of Motor Traffic website hit by cyber attack; services uninterrupted
Article Content

- •The DMT website was reportedly hit by a cyber attack on the night of 21 November 2026.
- •The DMT says its services, including appointments via the online portal and hotline, continue without interruption.
- •Newswire reports the Narahenpita office operations were not affected and continue as usual.
- •The articles do not disclose the attack method, the attacker, or any data impact.
The Department of Motor Traffic (DMT) in Sri Lanka announced that its official website was targeted by a cyber attack on the night of 21 November 2026, according to Daily Mirror. The DMT says services will continue without interruption and advised the public to keep booking appointments through its online portal or by calling its hotline on 0112 117 116. Newswire reports that the attack did not affect normal operations at the department's Narahenpita office, and services there are to continue as usual on Monday. Neither article names the attack method, the attackers, or the extent of any data exposure. Neither article reports any compromise of systems beyond the public website. The current status is that the website was attacked, and both outlets report that operations are continuing.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Department Of Motor Traffic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Am I affected if I need DMT services?
Has any data been compromised?
How should I book appointments now?
Continue Reading
 Critical Apache Roller RCE Vulnerability Actively Exploited in the Wild Apache has issued a warning regarding a critical remote code execution (RCE) vulnerability in Apache Roller, tracked as CVE-2026-129448, which is actively being exploited. This flaw affects versions 4.0.0 through 6.1.4 and allows unauthenticated attackers to execute arbitrary code via the XML-RPC endpoint. The…