 Bhaskarenglish.In
Starlink's Security Compliance Delays in India Amid Competition
Article Content

- •Starlink submitted security documents last among three providers in India.
- •All three companies have licenses but await regulatory approvals.
- •Spectrum allocation and pricing remain unresolved issues.
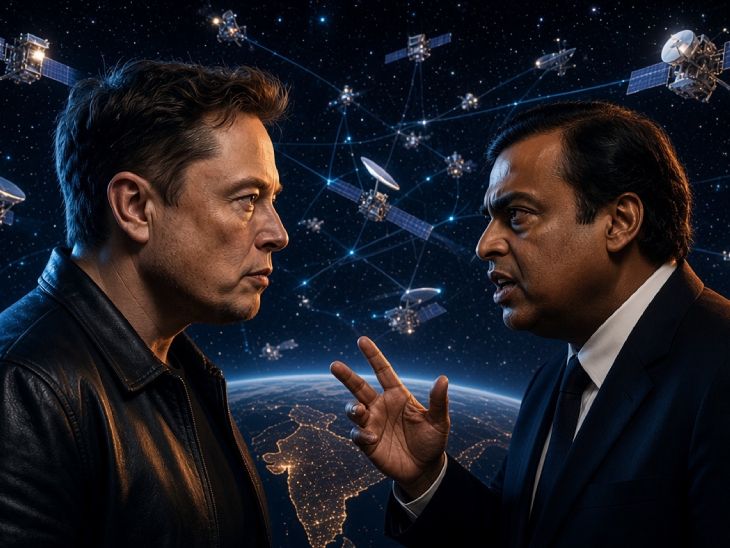
Elon Musk's Starlink was the last of three satellite internet providers in India to submit security compliance documents, following OneWeb and Jio. All three companies have received necessary licenses but are pending regulatory and security approvals before launching services. This situation arises after Musk alleged that certain industrialists are attempting to block Starlink's entry into the Indian market. The Indian government has rejected these claims, asserting that the licensing process is transparent and welcoming to all companies. Key issues delaying the launch include spectrum allocation and pricing, which have yet to be finalized. Starlink's infrastructure reportedly complies with India's security regulations, ensuring user data remains within the country. The competitive landscape includes major players like Airtel-backed OneWeb and Reliance-backed Jio, with customer choice expected to dictate market success.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What are the main delays for Starlink's launch?
How does the Indian government view Starlink's entry?
What is the status of security compliance for the providers?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…