 Cthb.Osce
OSCE Calls for Action Against Trafficking for Forced Criminality and Cyber Scams
Article Content

- •OSCE calls for renewed efforts to combat trafficking for forced criminality and cyber scams.
- •Victims are often coerced into fraud through threats and debt bondage.
- •International cooperation and public-private partnerships are essential to tackle this issue.
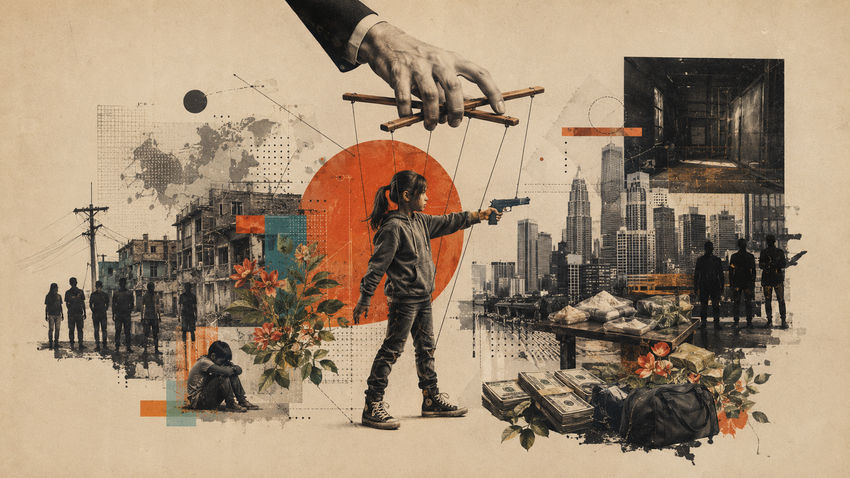
On July 30, 2026, the OSCE leadership urged for stronger measures to combat trafficking for forced criminality, coinciding with World Day against Trafficking in Persons. The call highlights the growing trend of criminal networks exploiting victims through deceptive job advertisements and coercing them into cyber scams. Victims are often transported across borders and compelled to commit fraud under threats and debt bondage. The OSCE emphasizes the need for enhanced public-private partnerships and international cooperation to dismantle these criminal networks. The organization stresses that victims should be recognized as such and not prosecuted as offenders. Front-line responders, including law enforcement and social protection institutions, must be equipped to identify trafficking indicators. The theme for this year, 'Trapped behind the scam,' reflects the urgency of addressing this evolving threat. The OSCE aims to strengthen victim-centered responses to protect those exploited by organized crime.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…