 En.Apa.Az
Türkiye and Japan to Enhance Defense Cooperation on Drone Technology
Article Content
Browse articles 
- •Türkiye seeks to deepen defense cooperation with Japan, particularly in drone technology.
- •Minister Hakan Fidan emphasized the complementary capabilities of both countries in UAV production.
- •Negotiations for a social security agreement between Türkiye and Japan have shown positive progress.
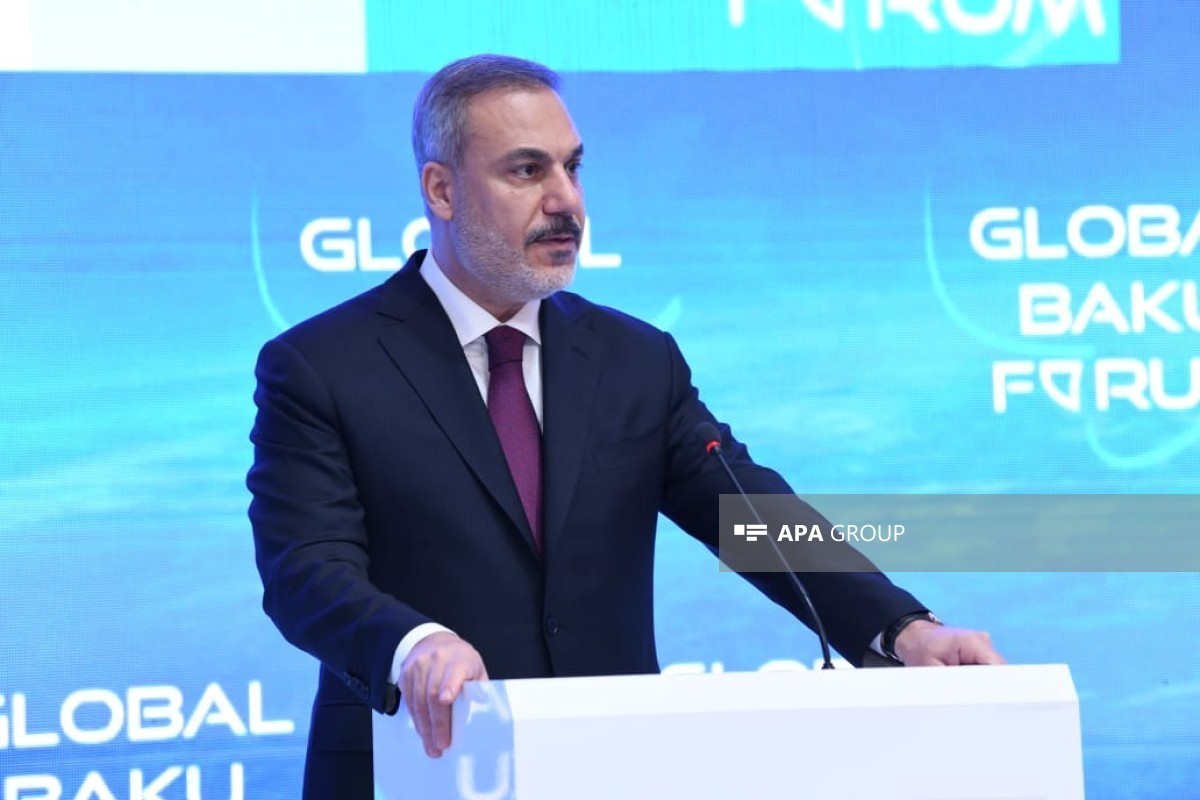
Türkiye aims to strengthen its defense industry collaboration with Japan, focusing on unmanned aerial vehicles (UAVs). Turkish Foreign Minister Hakan Fidan highlighted the complementary capabilities of both nations, emphasizing potential joint development and co-production of drones. He noted that Türkiye's UAV technologies have been effective in various operational scenarios, particularly in coastal and border security. Progress has also been made in negotiations for a social security agreement between the two countries. The discussions reflect a growing interest in defense partnerships among middle-power nations.
Ask AI about this cluster
Answers cite the sources they use
Updated 113d ago How this analysis works
Timeline
2026-05-30
Fidan's interview published
Turkish Foreign Minister Hakan Fidan discussed defense cooperation prospects with Japan, focusing on drones.
Asia.Nikkei2026-05-31
Türkiye announces defense cooperation intent
Türkiye's Foreign Minister reiterated the country's interest in enhancing defense ties with Japan, particularly in UAVs.
En.Apa.AzMore articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…