 Latimes
Three Suspects Wanted in Burglary of NFL Rookie's Home
Article Content

- •Three suspects have warrants issued for the burglary of NFL rookie Max Iheanachor's home.
- •The burglary occurred on August 26, 2026, with losses estimated at $200,000.
- •Security footage and rental records were crucial in identifying the suspects.
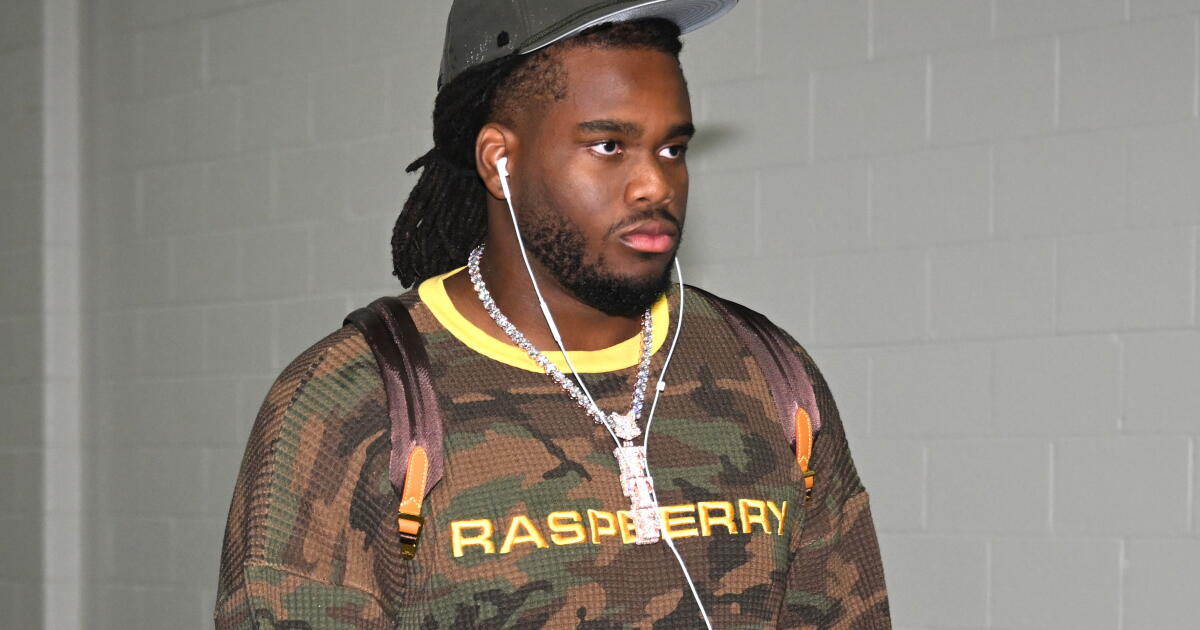
Pittsburgh police have issued warrants for three Los Angeles residents in connection with the burglary of Steelers rookie Max Iheanachor's home, which occurred on August 26, 2026. The suspects, Winter Brantley, Andre Castle Jr., and Lamar Stewart, face multiple charges including burglary and theft, with approximately $200,000 worth of jewelry and designer bags reported stolen. Security footage and rental car records were used to identify the suspects, who allegedly used an Audi SUV during the crime. Iheanachor, who moved to L.A. from Nigeria at age 13, reported the break-in a day before the Steelers' final preseason game. His roommate, Ashley Brantley, is related to one of the suspects and indicated familial disputes may have played a role in the incident. The U.S. Marshals Service is assisting in the search for the suspects.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
Who are the suspects?
What was stolen during the burglary?
What charges are the suspects facing?
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…
 Critical CVE-2026 Flaws in Control Web Panel Lead to Account Takeover Risks Control Web Panel (CWP) versions prior to 1.30.6 are affected by two critical vulnerabilities, CVE-2026-124020 and CVE-2026-124021, both disclosed on 2026-11-13. CVE-2026-124020 allows attackers to exploit a host header injection in the password recovery process, potentially leading to account takeover via a poisoned…