 www.nbcnews.com
UK Defense Secretary Resigns Over Military Spending Crisis Amid Rising Threats
Article Content

- •John Healey resigned due to insufficient military funding amid rising global threats.
- •The UK government's Defense Investment Plan is criticized for not meeting defense needs.
- •Al Carns also resigned, emphasizing concerns over military readiness and resource allocation.
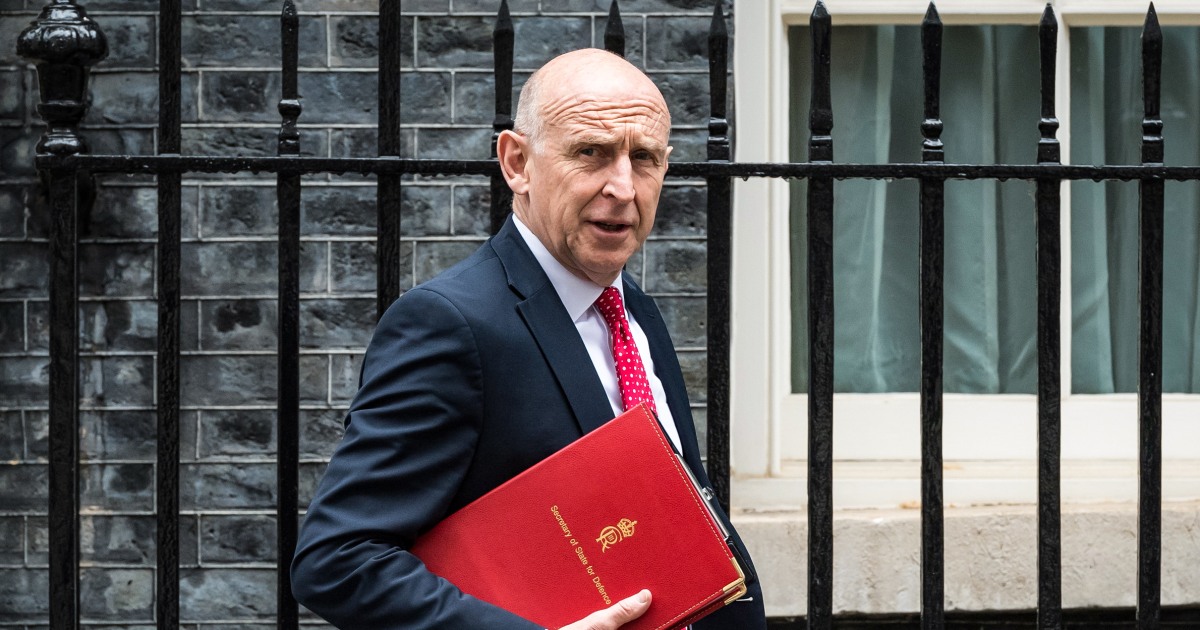
UK Defense Secretary John Healey resigned on June 11, 2026, citing inadequate military funding amid escalating global threats, including the Iran war and Russia's invasion of Ukraine. He criticized the government's Defense Investment Plan for falling short of necessary resources, arguing that defense spending should reach 3-3.5% of GDP instead of the planned 2.68% by 2030. Following his resignation, junior minister Al Carns also stepped down, expressing concerns about military readiness. Prime Minister Keir Starmer appointed Dan Jarvis as the new defense secretary, but internal dissent within the Labour Party is growing. The resignations highlight significant gaps in the UK's military preparedness and funding, raising questions about the country's defense strategy in a changing global landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track BAE Systems in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…