 Theguardian
UK Military Authorized to Interdict Russian Shadow Fleet in Waters
Article Content

- •UK armed forces are now authorized to board sanctioned Russian vessels in UK waters.
- •The shadow fleet consists of over 600 vessels evading sanctions by using false flags.
- •The move aims to cut off funding for Russia's military operations in Ukraine.
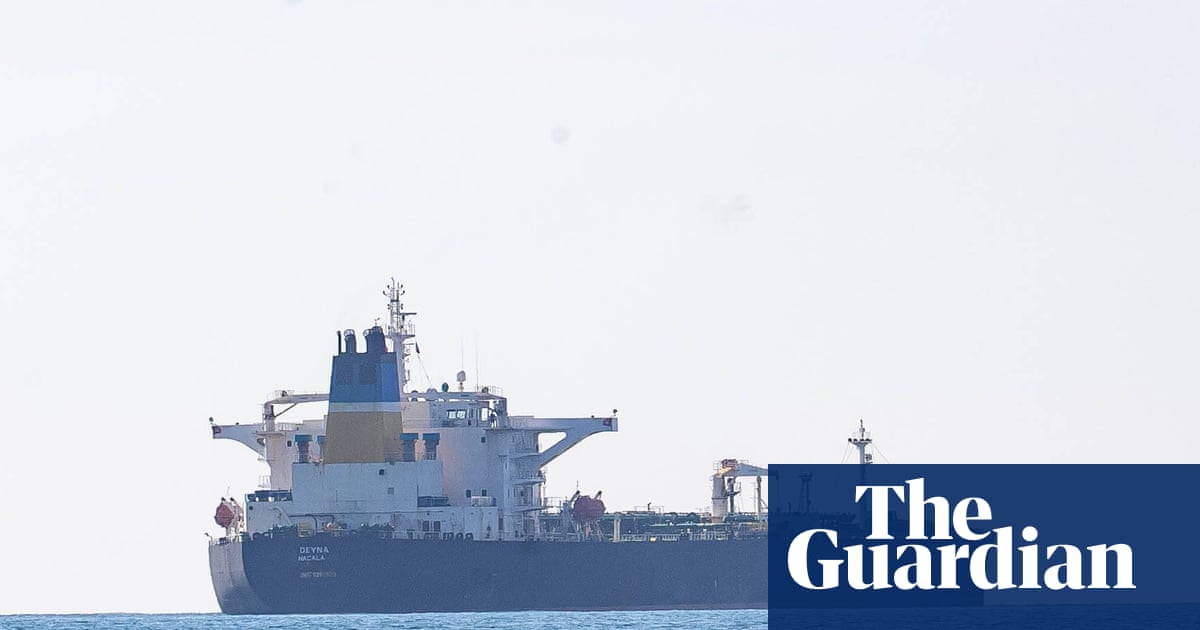
The UK government has authorized its armed forces to board and detain Russian shadow fleet vessels in UK waters as part of escalating actions against Russia's evasion of sanctions related to its war in Ukraine. This decision follows months of preparation and training for military personnel, and comes as the Prime Minister attends the Joint Expeditionary Force Summit in Finland. The shadow fleet consists of vessels operating under false flags to transport Russian oil, with over 600 vessels currently under sanctions from the EU, UK, and US. The UK aims to disrupt these operations, which are believed to fund Russia's military efforts. The Royal Navy has been actively tracking these vessels, and the new measures will allow for direct action against them. The UK's actions are supported by allies in the region, including Finland, Sweden, and Estonia, who have also engaged in operations against these ships. The situation remains tense, with Russia warning of potential military responses to such interdictions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (16)
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…